Enterprise Resource Security Mastering Cryptographic Key Lifecycles
Top News

Post-Quantum Cryptography in Industry: Why Long-Lived Systems Need Crypto-Agility

October 26, 2026

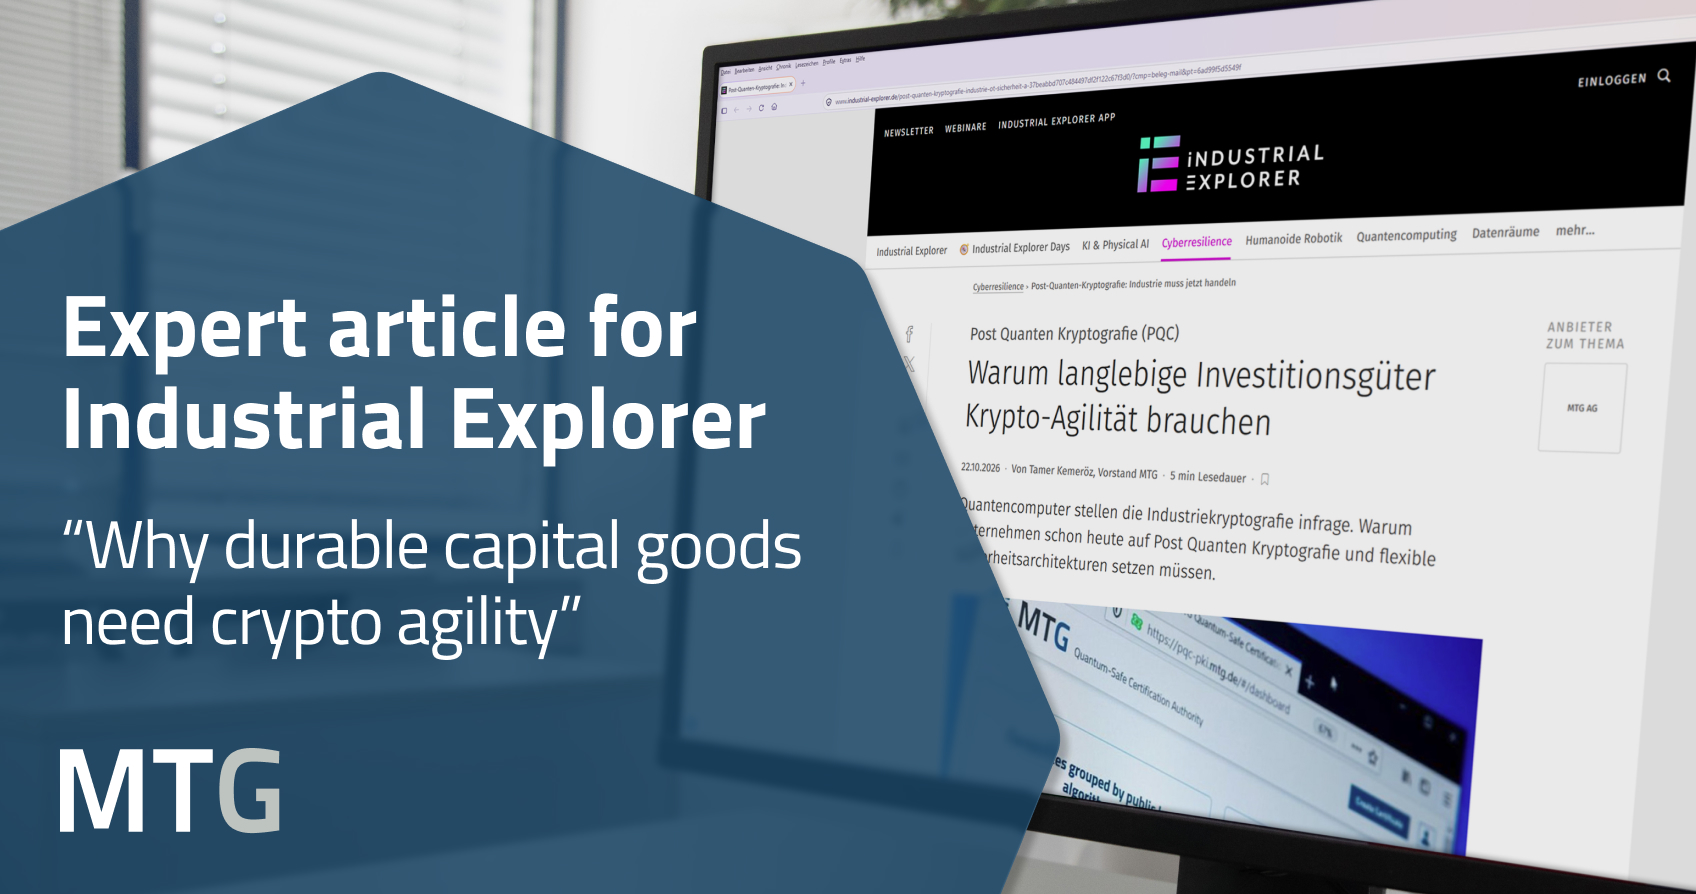
Expert article for Industrial Explorer: “Why durable capital goods need crypto agility”

Machines and control systems often operate for decades, but their cryptography has a significantly shorter lifespan. Tamer Kemeröz, Member of the Board at MTG, explains in Industrial Explorer why the industry should adopt post-quantum cryptography now and what manufacturers can do specifically.
A machine controller installed in a factory today could still be in operation as late as 2056. The encryption methods that protect it today could be long outdated by then. In our expert article, Tamer Kemeröz describes this lifespan paradox. He explains why manufacturers of control systems, machines, and OT infrastructures should make the cryptographic foundation of their products quantum-secure today.

TK, PKI-Experte bei MTG

Why does the quantum risk for industrial systems begin today?

Cryptographic methods such as RSA or ECC (Elliptic Curve Cryptography) are currently used in industry to secure certificates, firmware updates, and machine identities. A powerful quantum computer could break these algorithms. When that will happen remains a matter of debate. However, due to the “harvest now, decrypt later” approach, the risk begins today: Attackers can intercept and store encrypted data now and decrypt it later. This affects, for example, design data, firmware signatures, and access keys to industrial systems.

The crucial question for manufacturers is therefore not when the quantum computer will arrive, but how long today’s cryptography must remain secure. Given a product lifecycle of about 20 years, the answer is: at least until the mid-2040s. Leading technology companies are demonstrating that the risk is drawing nearer: Google has moved up its own PQC migration deadline from the original 2031–2035 to 2029, and IBM expects a fault-tolerant quantum computer by 2029.

What role do the Cyber Resilience Act and NIS2 play?

With the EU’s NIS2 Directive and the Cyber Resilience Act (CRA), IT and OT security become a matter of liability for corporate management. The CRA requires manufacturers of networked products to ensure cybersecurity throughout the entire product lifecycle. According to Tamer Kemeröz, anyone offering long-lasting control systems or IoT devices whose cryptography cannot be retrofitted to be quantum-secure in the field risks future sales bans in the EU single market and fines. MTG AG estimates that PQC will thus effectively become a compliance requirement for long-lasting industrial products.

What standards for post-quantum cryptography already exist?

Post-quantum cryptography is already standardized and in use. The U.S. National Institute of Standards and Technology (NIST) published the first PQC standards in 2024: ML-KEM (FIPS 203) for key exchange, as well as ML-DSA (FIPS 204) and SLH-DSA (FIPS 205) for digital signatures. Google is already using PQC in Chrome and its own cloud and is integrating PQC signatures into Android 17. In Germany, MTG AG is working with the BSI (Federal Office for Information Security) and other industry partners on standards for quantum-secure email encryption. One result is the PQC extension of OpenPGP, which was published as Internet Standard RFC 9980.

Why is PQC a matter of PKI architecture in the industry?

In the industrial context, post-quantum cryptography is not only about encrypted communication but, above all, about identity: How does a control system know that a firmware update really comes from the manufacturer? Secure boot, firmware signing, device certificates, and authentication in the fieldbus rely on public-key infrastructures (PKI). If the cryptographic foundation of a PKI is vulnerable, the entire chain of trust is affected—including devices that were shipped years ago. PQC is therefore not merely a cryptographic update, but a matter of the entire PKI architecture.

What is crypto-agility, and why do manufacturers need it?

Crypto-agility is a system’s ability to quickly replace cryptographic algorithms, keys, and certificates without disrupting system operations. If this interchangeability is not built into the product design from the outset, retrofitting to PQC later on is virtually impossible. This poses a challenge in the industry: control systems are sometimes only accessible to a limited extent; with IoT devices, each device must be migrated with its own certificate; and small chips with just a few kilobytes of memory reach their storage limits when dealing with the significantly larger PQC keys and signatures.

What should manufacturers do now?

For Tamer Kemeröz, PQC in the industry is first and foremost a planning task. He recommends three initial steps:

  • Assess the current state: Where in the portfolio is each cryptographic method used, and what is its expected lifespan?
  • Review PKI: What PKI and certificate structures are in place, and are root certificates and firmware signing designed to be cryptographically agile?
  • Test hybrid approaches: For new developments, implement classical and PQC algorithms in parallel (hybrid cryptography).

Starting early determines whether the migration can be planned calmly or must be carried out later under time pressure.

Learn more now

Read the full technical article in Industrial Explorer. Do you have questions about the PQC migration of your products? Contact us.

Frequently Asked Questions (FAQs)

Why is post-quantum cryptography particularly relevant for industry?

Industrial control systems and machines often remain in use for decades. A control system installed today could still be in operation in 2056. Its cryptography must therefore remain secure even if powerful quantum computers are able to break today’s methods, such as RSA or ECC.

What does “Harvest now, decrypt later” mean?

With “Harvest now, decrypt later,” data is intercepted and stored today so that it can be decrypted later using a powerful quantum computer. The risk therefore begins not only when such a quantum computer becomes available, but already today.

What does the Cyber Resilience Act have to do with post-quantum cryptography?

The Cyber Resilience Act (CRA) requires manufacturers of connected products to ensure cybersecurity throughout the entire product lifecycle. According to MTG AG’s assessment, post-quantum cryptography will thus effectively become a compliance requirement in product development for long-lasting industrial products.

What does crypto-agility mean?

Crypto-agility is a system’s ability to quickly replace cryptographic algorithms, keys, and certificates without disrupting system operations. This is particularly challenging in industrial settings because control systems are sometimes only partially accessible, and many devices must be migrated individually.

Downloads & Links

Share This News

What can we do for you?

For further information feel free to contact us!

WordPress Cookie Plugin by Real Cookie Banner