DARZ Managed PKI & CLM
PKI & Certificate Management Made Easy –
Automation included
Organizations today use an increasing number of certificates, while security and compliance requirements continue to grow. Without a structured PKI and certificate management approach, it becomes increasingly difficult to maintain visibility over certificates, their lifetimes, and associated permissions. Certificate Lifecycle Management (CLM) provides transparency and control. Certificates can be centrally managed, automatically deployed, and renewed on time. Our system supports key PKI automation protocols including SCEP, ACME, EST, and CMP. Public certificates with increasingly shorter validity periods can also be efficiently managed with an automated CLM system. As a result, administrative effort is significantly reduced, and the risk of expired certificates is minimized. Regulatory requirements such as the NIS2 Directive and the Digital Operational Resilience Act further increase the need for structured certificate management. For affected organizations, a Managed PKI provides a fast and straightforward way to reliably meet these requirements.
Easily Extend Microsoft PKI with CLM
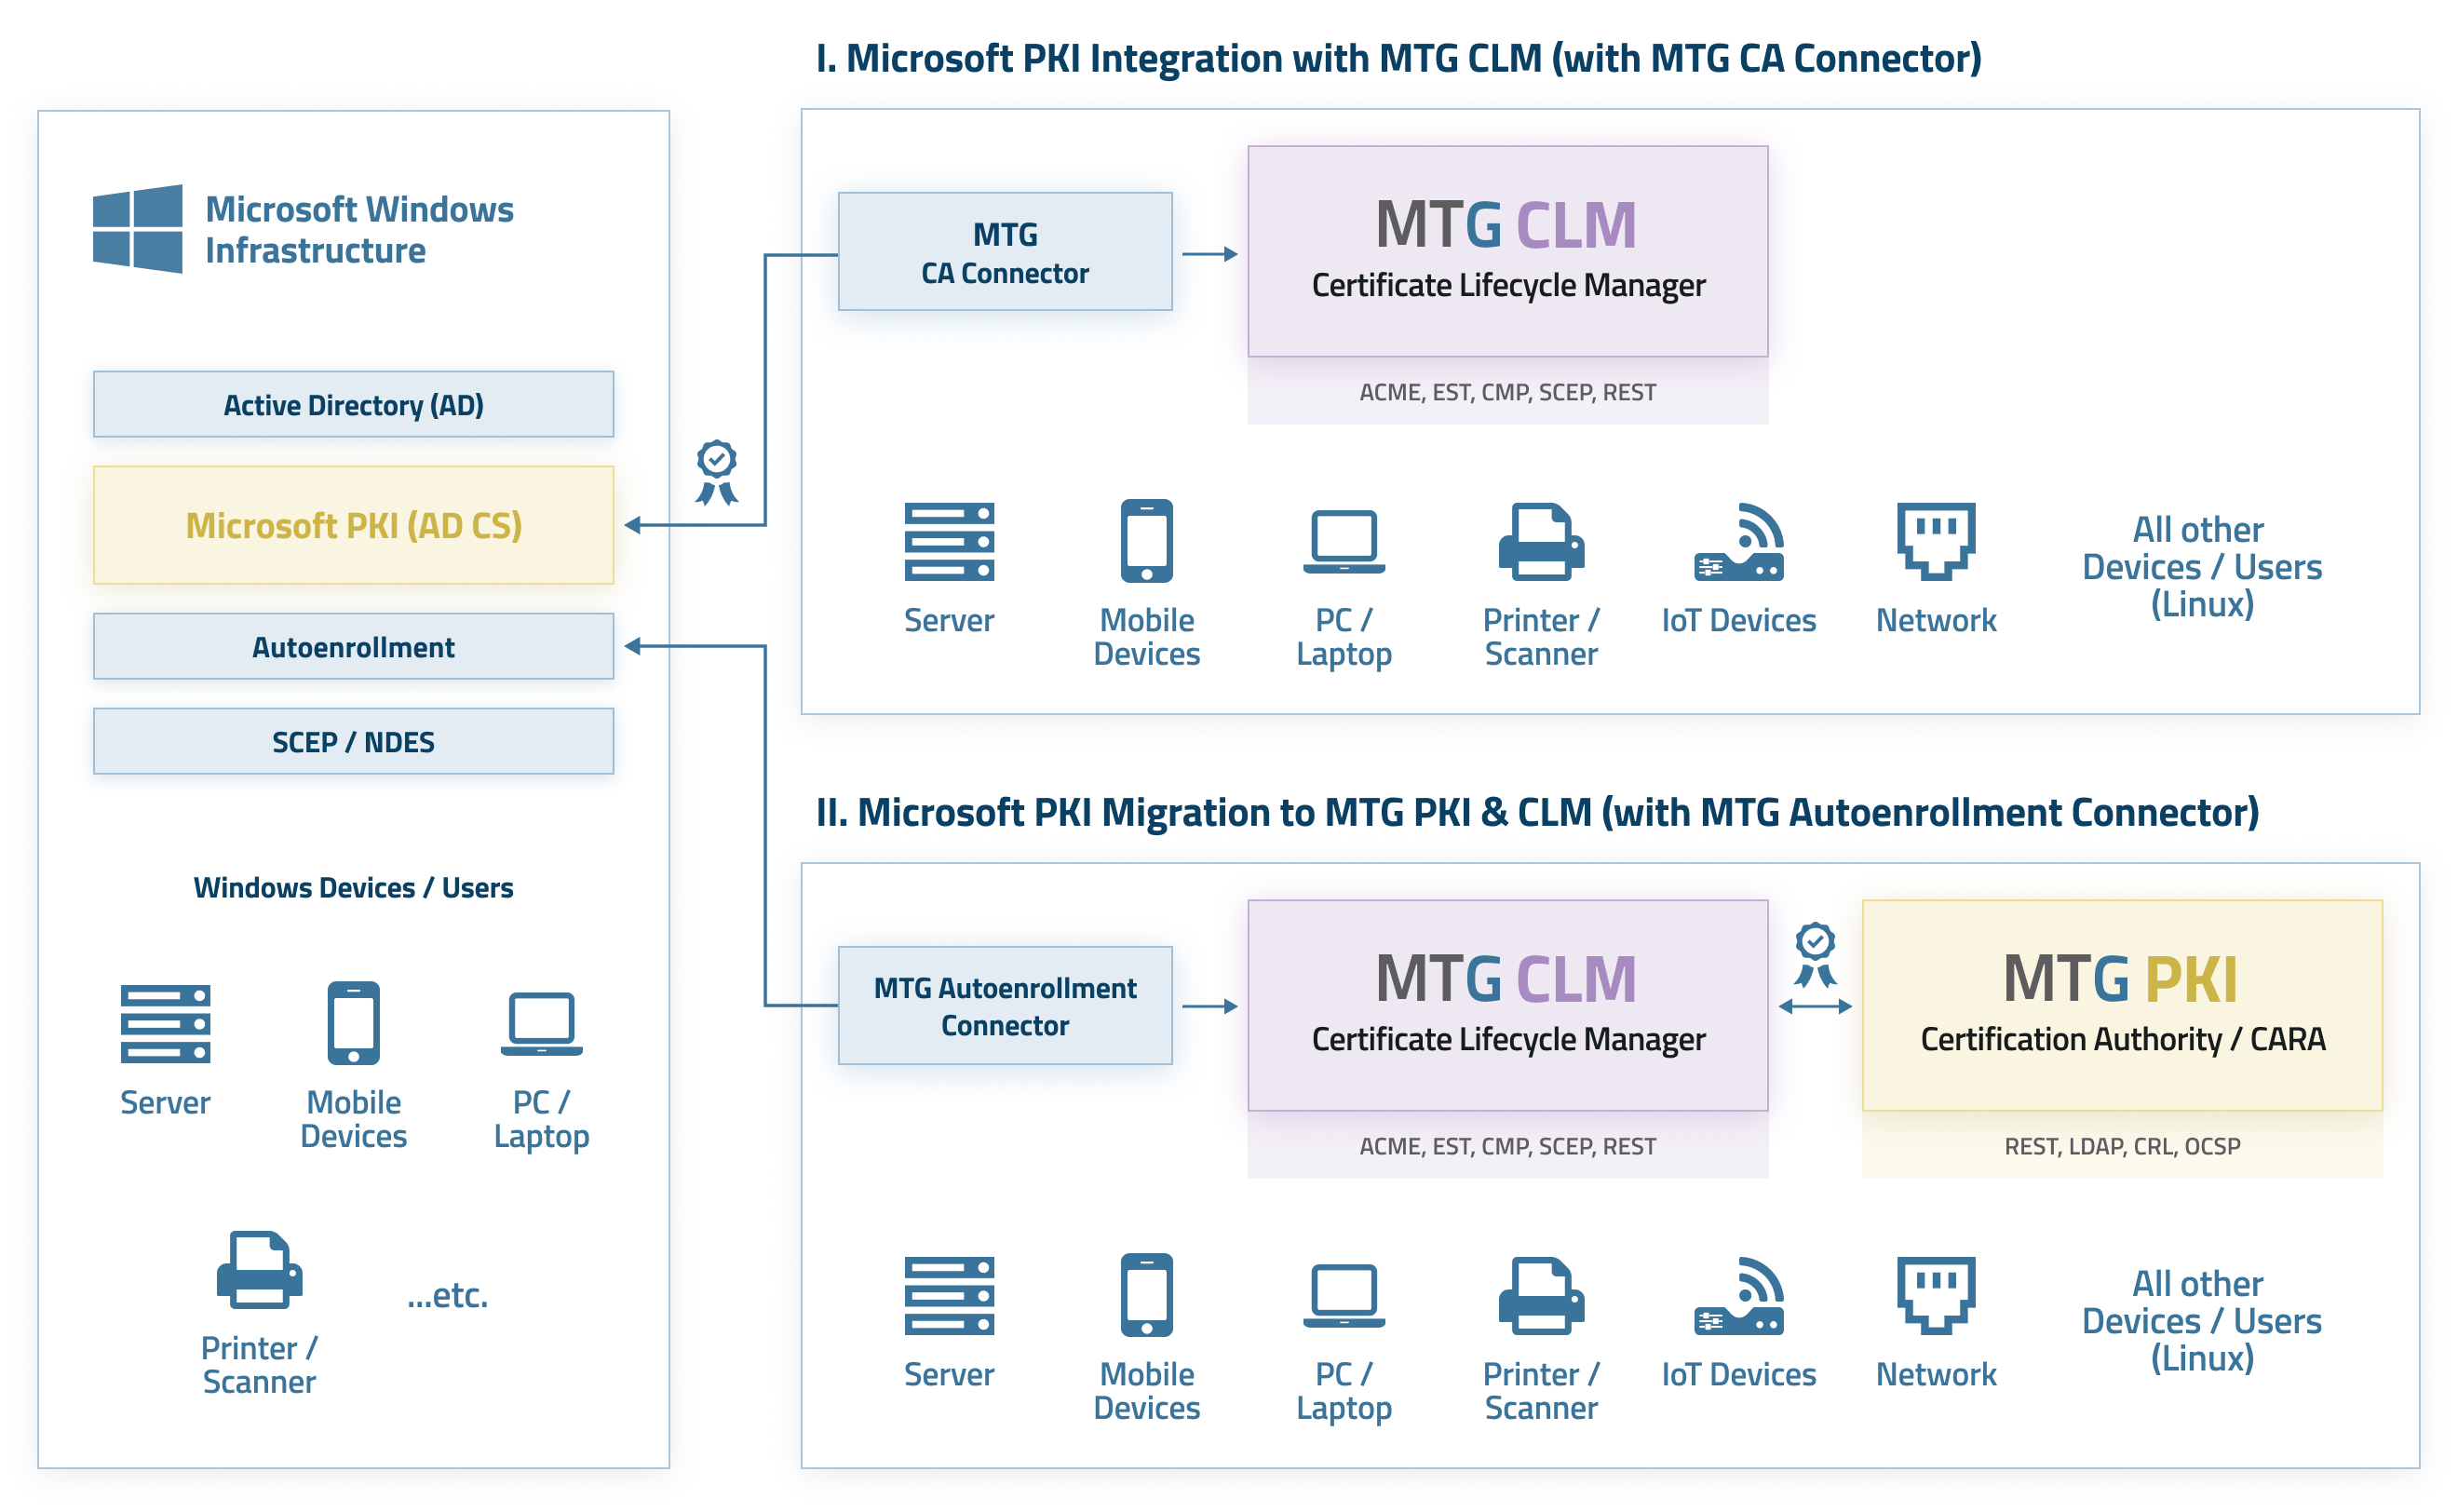
Microsoft PKI (AD CS) is widely used but does not include built-in certificate management. MTG CLM complements this capability by extending the existing Microsoft PKI with comprehensive, modern Certificate Lifecycle Management functionality. All essential certificate management processes can be implemented quickly and easily without replacing the existing Microsoft PKI. This allows organizations to benefit from a powerful CLM solution without introducing additional requirements for their own infrastructure.