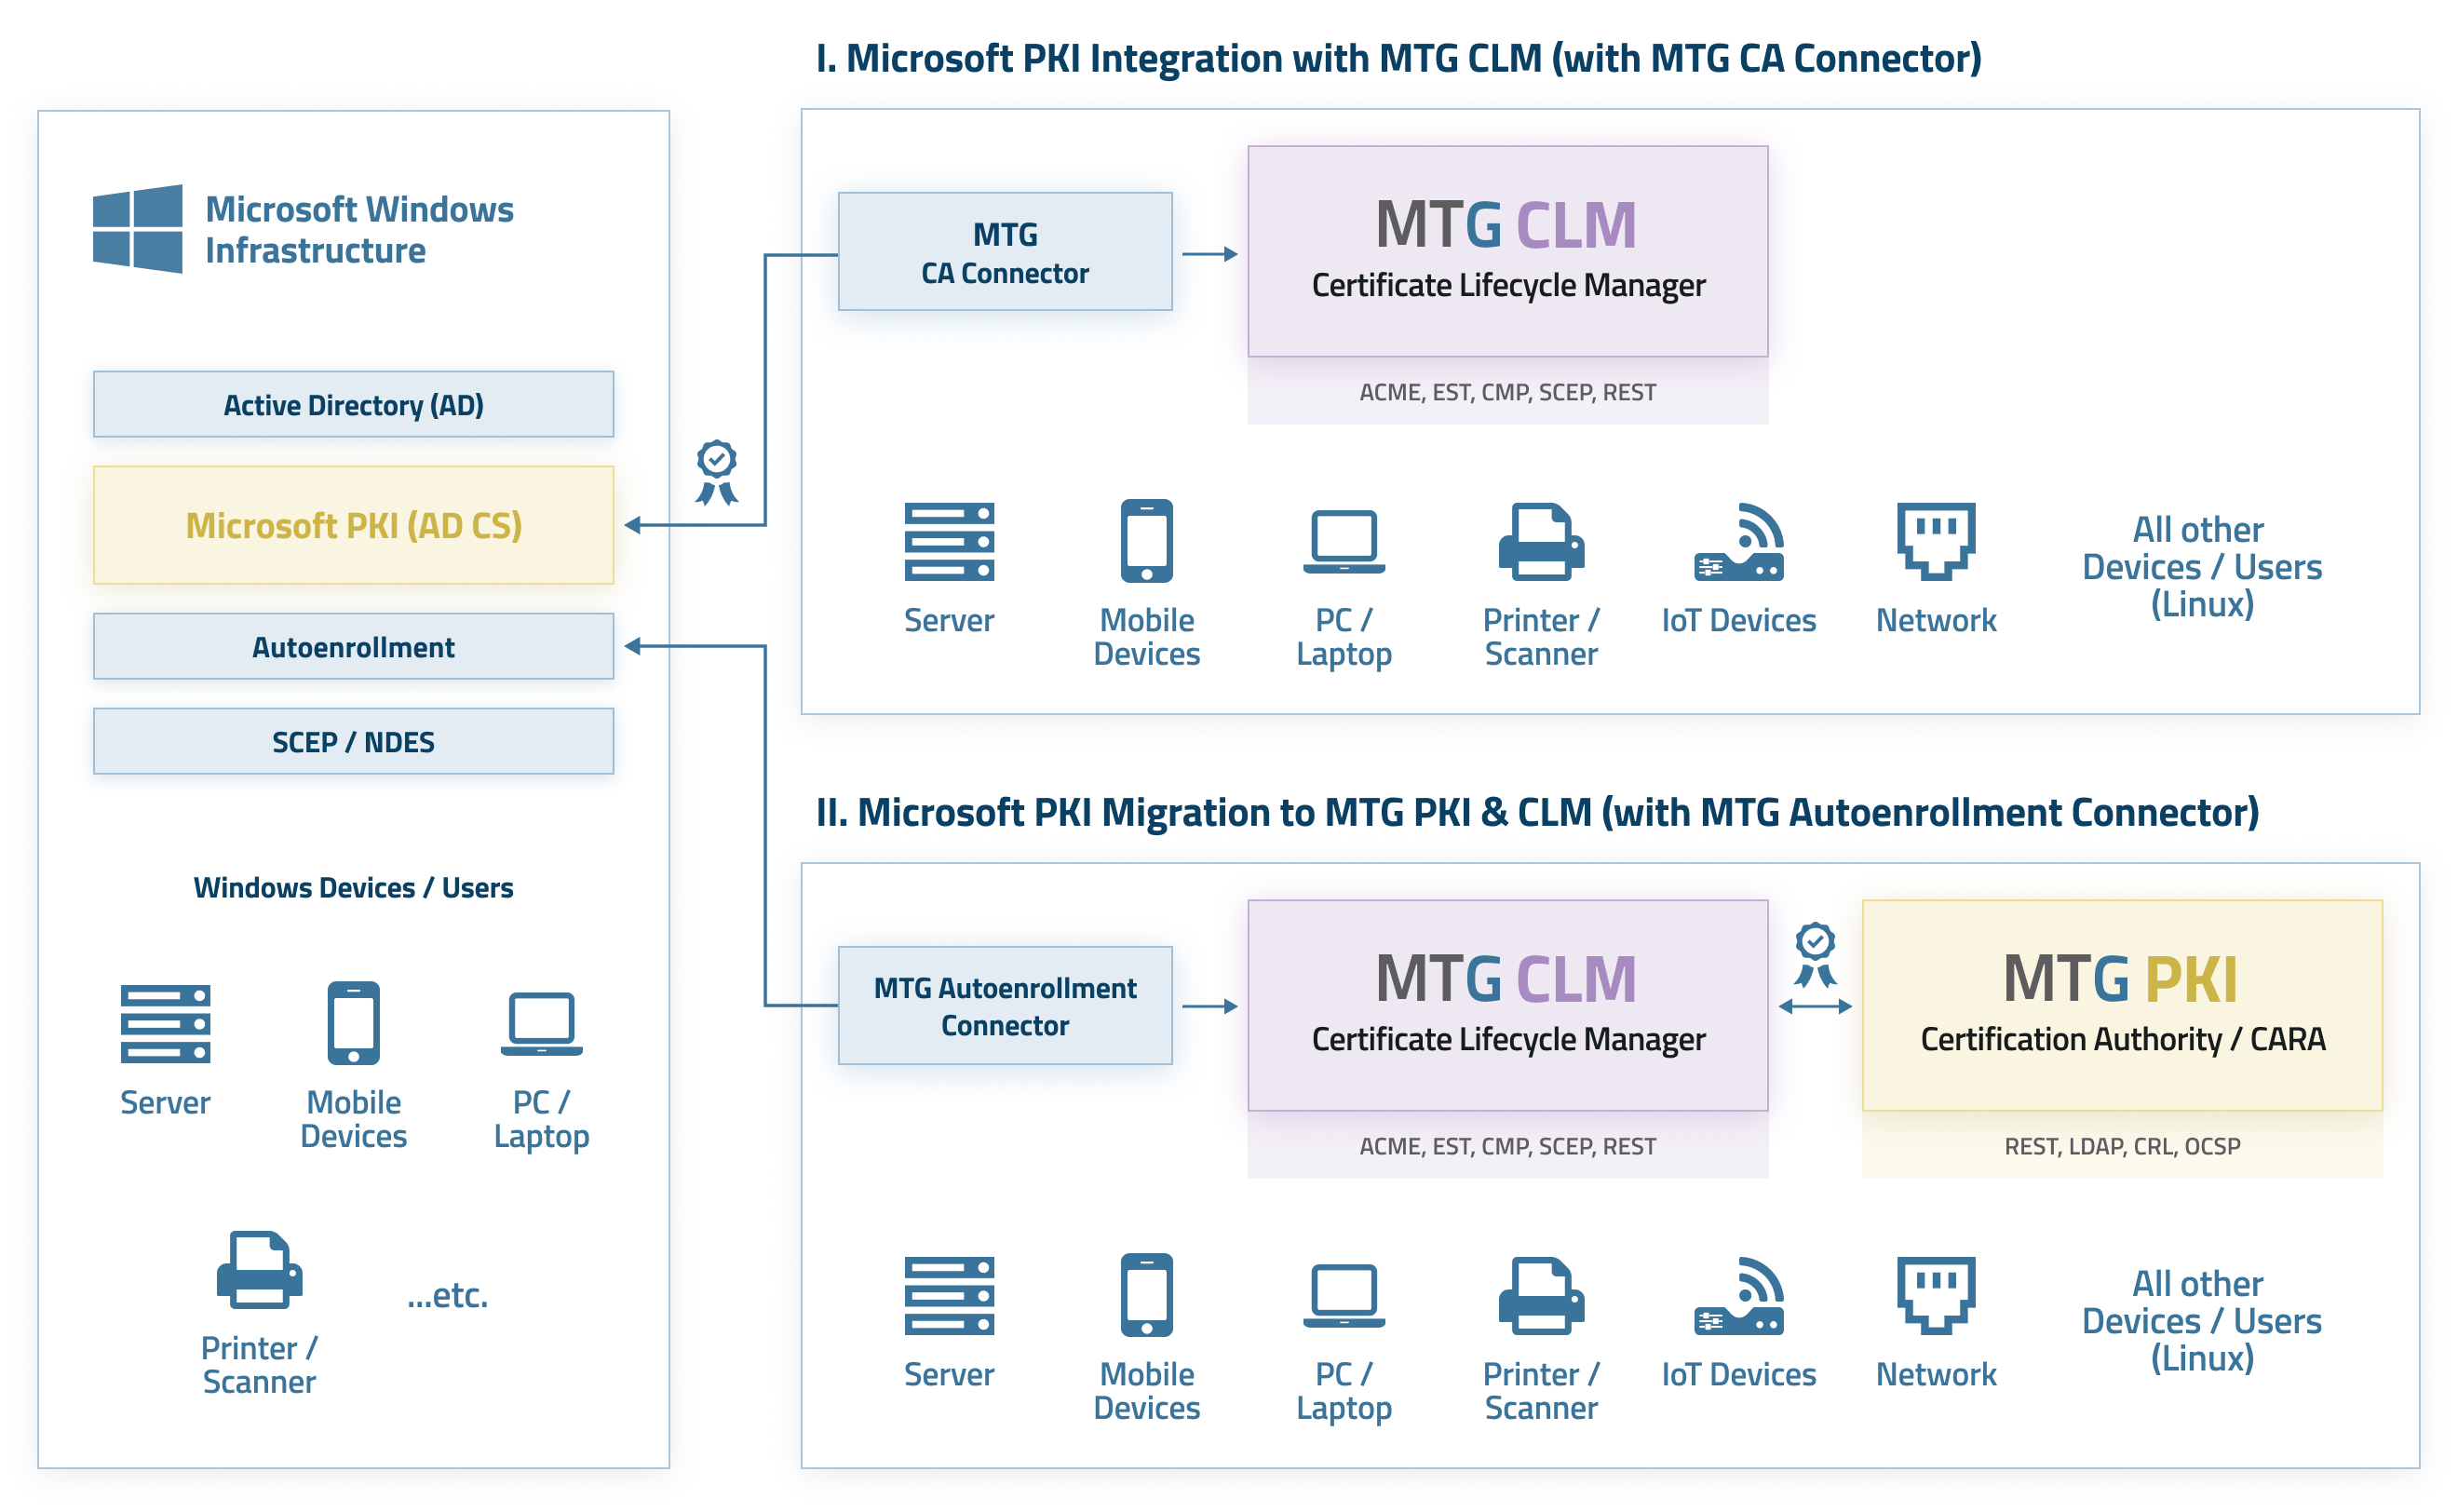
Yes, with the CLM Autoenrollment Connector, you can continue to use established Microsoft autoenrollment processes when migrating from Microsoft AD CS to MTG Corporate PKI. The Connector integrates MTG Corporate PKI into the existing Microsoft Active Directory environment and enables automated certificate request, renewal, and deployment through established Windows mechanisms.
The specific migration effort depends on your existing Active Directory and PKI configuration, the certificate templates in use, and your individual use cases. Preparatory changes may therefore be required. MTG supports you with the migration from Microsoft AD CS to MTG Corporate PKI and with integration into your existing Microsoft environment.
Alternatively, an existing Microsoft CA can continue to operate and be connected to MTG CLM through the Microsoft CA Certificate Provider. In this scenario, Microsoft CA remains the issuing CA while you benefit from the extended Certificate Lifecycle Management capabilities of MTG CLM.
For evaluation purposes, a locally installable test simulator can also be provided for the Autoenrollment Connector.