
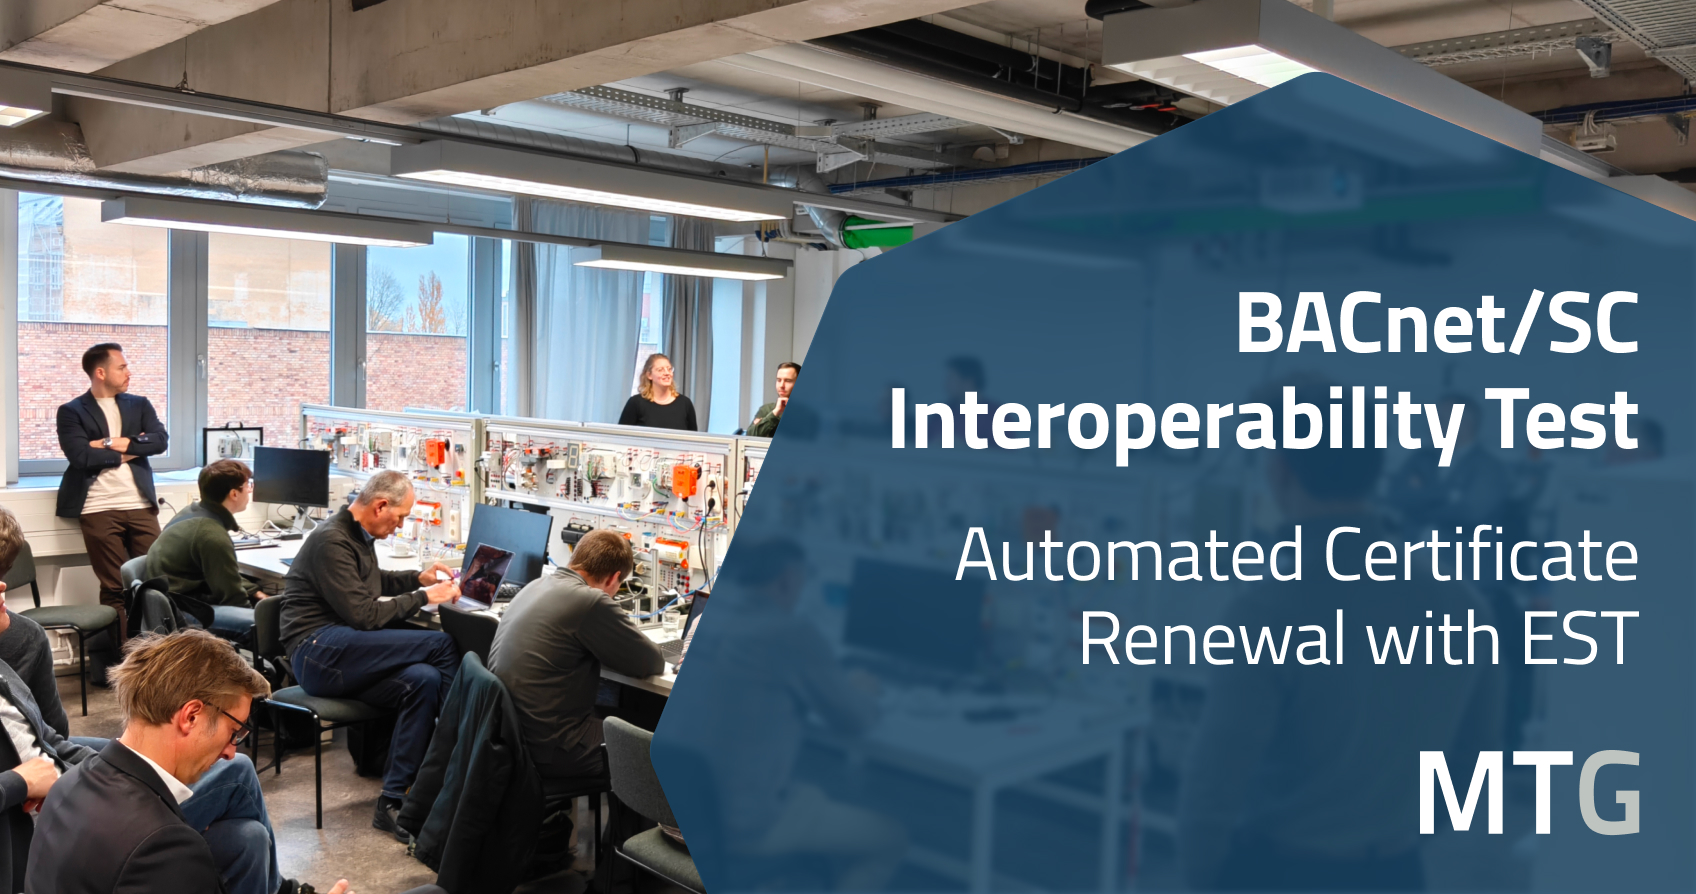
In early November, building automation manufacturers gathered at HTW Berlin for the BACnet/SC interoperability test. Together with WAGO, we demonstrated there that device certificate renewal can be automated using the EST standard protocol.
November 17, 2026
In early November, building automation manufacturers gathered at HTW Berlin for the BACnet/SC interoperability test. Together with WAGO, we demonstrated there that device certificate renewal can be automated using the EST standard protocol.
BACnet Secure Connect (BACnet/SC) secures communication in building automation using TLS encryption and digital certificates. However, the standard does not specify how these certificates are installed in devices or how they are renewed: A public-key infrastructure (PKI) with a certification authority and registration authority is not defined in BACnet/SC. For operators of large properties, certificate management—which is usually done manually—quickly becomes a hurdle.
The research project “BACnet Secure Connect – Further Development and Management for Critical Infrastructure” addresses this gap. The Federal Office for Building and Regional Planning (BBR) conducted the project in collaboration with HTW Berlin . For the interoperability test, manufacturers of field devices and controllers gathered at the HTW Berlin laboratory in Schöneweide. After two days of closed-door testing, the results were presented to the public on the third day.
The findings will be incorporated into a BBR guideline on secure BACnet communication with BACnet/SC. The guideline is intended to provide project managers and building owners in federal construction projects with practical steps and testing criteria.
The research project examines three technically distinct methods by which BACnet/SC devices obtain their certifications:
Manual, file-based exchange of certificate applications and certificates.
Suitable for: laboratory testing, preliminary acceptance, interim solution
The gateway handles the certificate processes and communicates with the MTG PKI via EST.
Suitable for: Devices without their own EST client, existing systems
The controller communicates directly with the MTG PKI via EST.
Suitable for: Devices with an integrated EST client
We had already presented the solution combining MTG Corporate PKI and MBS PKI Gateway at the 38th GLT User Conference. In Berlin, our focus was on the third approach: the direct EST connection.
On the public results day, November 6, Dr. Nina Bindel, Senior Project Manager at MTG AG, and Marvin Behrens (WAGO) presented the talk “Certificate Renewal with EST.” EST stands for Enrollment over Secure Transport (RFC 7030), an open standard protocol for the automated issuance and renewal of certificates. The presentation centered on a live demonstration using WAGO controllers that already natively support EST. The MTG Corporate PKI with an EST server served as the remote station. Also present was Dr. Evangelos Karatsiolis, Executive Cyber Security Expert at MTG AG, who represented MTG during the test days.
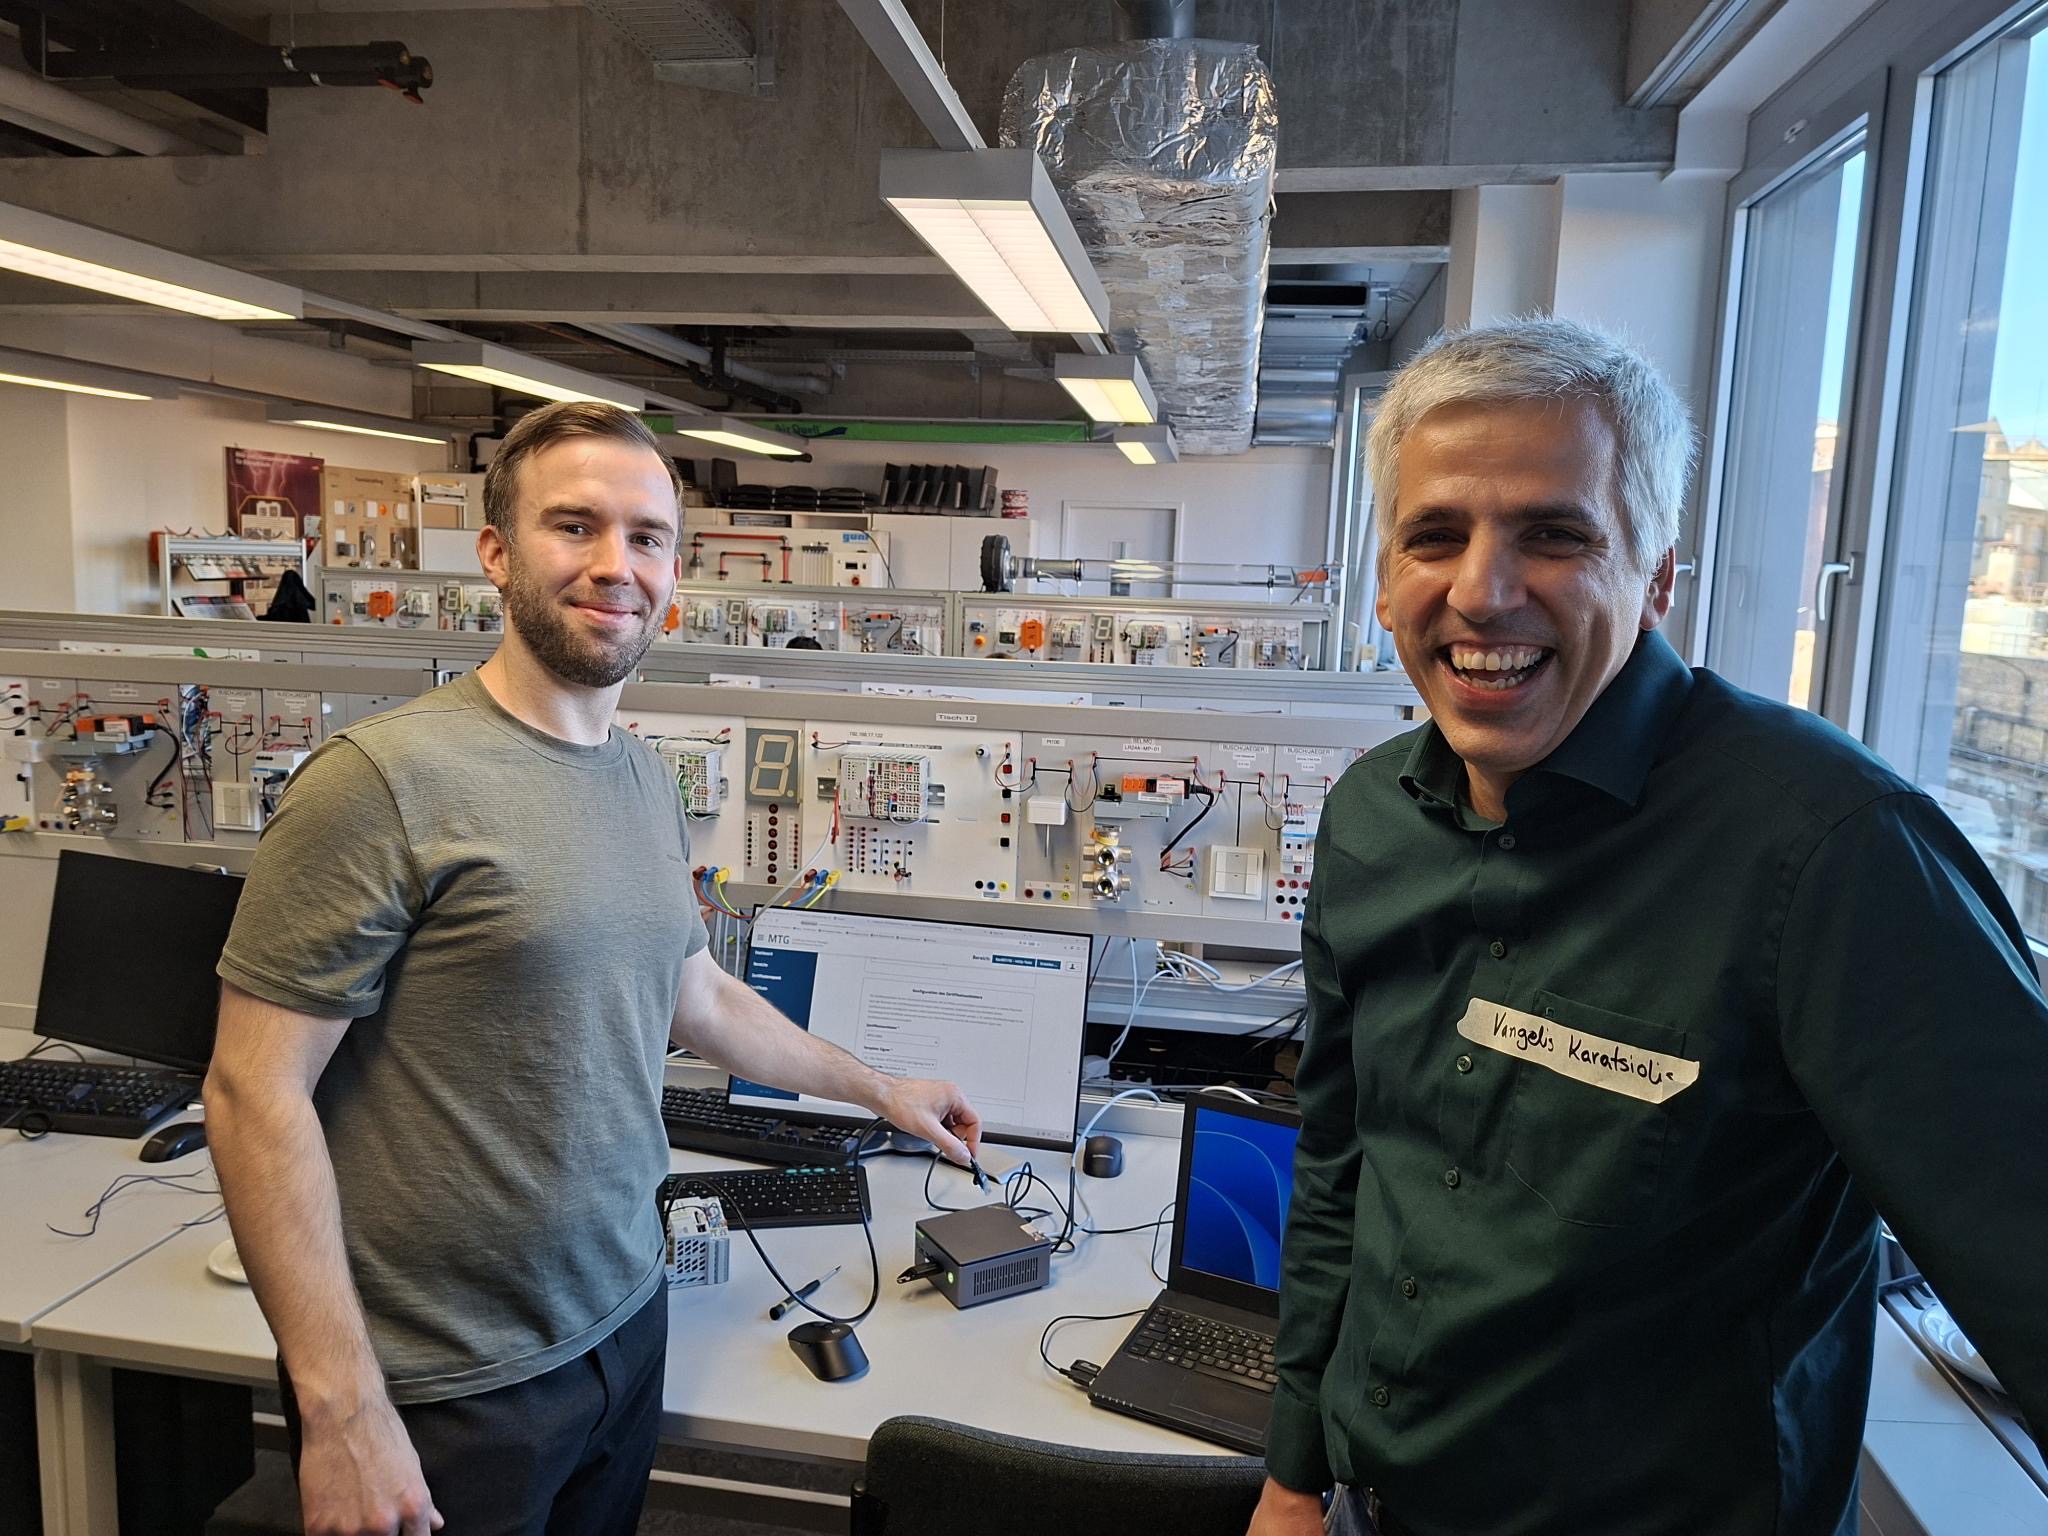
The demonstration was successful. The certificate renewal was fully automated via EST, and the private key never left the device.
The demo shows that when devices support EST, certificate management for BACnet/SC becomes predictable and scalable. Operators retain control over certificates and validity periods via their own PKI. For devices without an EST client, the MBS PKI Gateway provides an alternative solution.
For manufacturers of field devices and controllers, this sends a clear message: An integrated EST client makes devices ready for automated operation in large properties.
We would like to thank the BBR and HTW Berlin for organizing the event and providing the open test environment. Special thanks go to WAGO for the joint demonstration, as well as to all participating manufacturers for the constructive exchange.
Dr. Nina Bindel and our team are available to advise you on automated certificate renewal and our PKI solution for building automation.
Dr. Nina Bindel
Senior Project Manager, MTG AG
BACnet Secure Connect is an extension of the BACnet protocol for building automation. It encrypts communication using TLS and authenticates devices via certificates.
Each device requires a valid certificate that must be renewed regularly. However, the standard does not specify what the PKI should look like for this purpose. In large properties with many devices, manual management is error-prone and time-consuming.
Enrollment over Secure Transport (EST, RFC 7030) is a standardized protocol that allows devices to request and renew certificates over a TLS-secured connection. The private key remains on the device.
EST automates the request and renewal of certificates. There is no longer a need to exchange files manually or to monitor expiration dates manually. This reduces effort and the risk of downtime, especially in facilities with many devices.
In that case, a gateway handles the certificate processes. The MBS PKI Gateway integrates such devices and, in turn, communicates with the MTG Corporate PKI via EST.
Based on the research project, the Federal Office for Building and Regional Planning is developing guidelines for BACnet/SC in federal construction projects. These guidelines are intended to define roles, certificate workflows, and verification criteria.
Automated certificate management for BACnet/SC infrastructures.
Connects BACnet/SC devices without their own EST client to the PKI.
How MTG and MBS automate certificate processes for BACnet/SC.
For further information feel free to contact us!