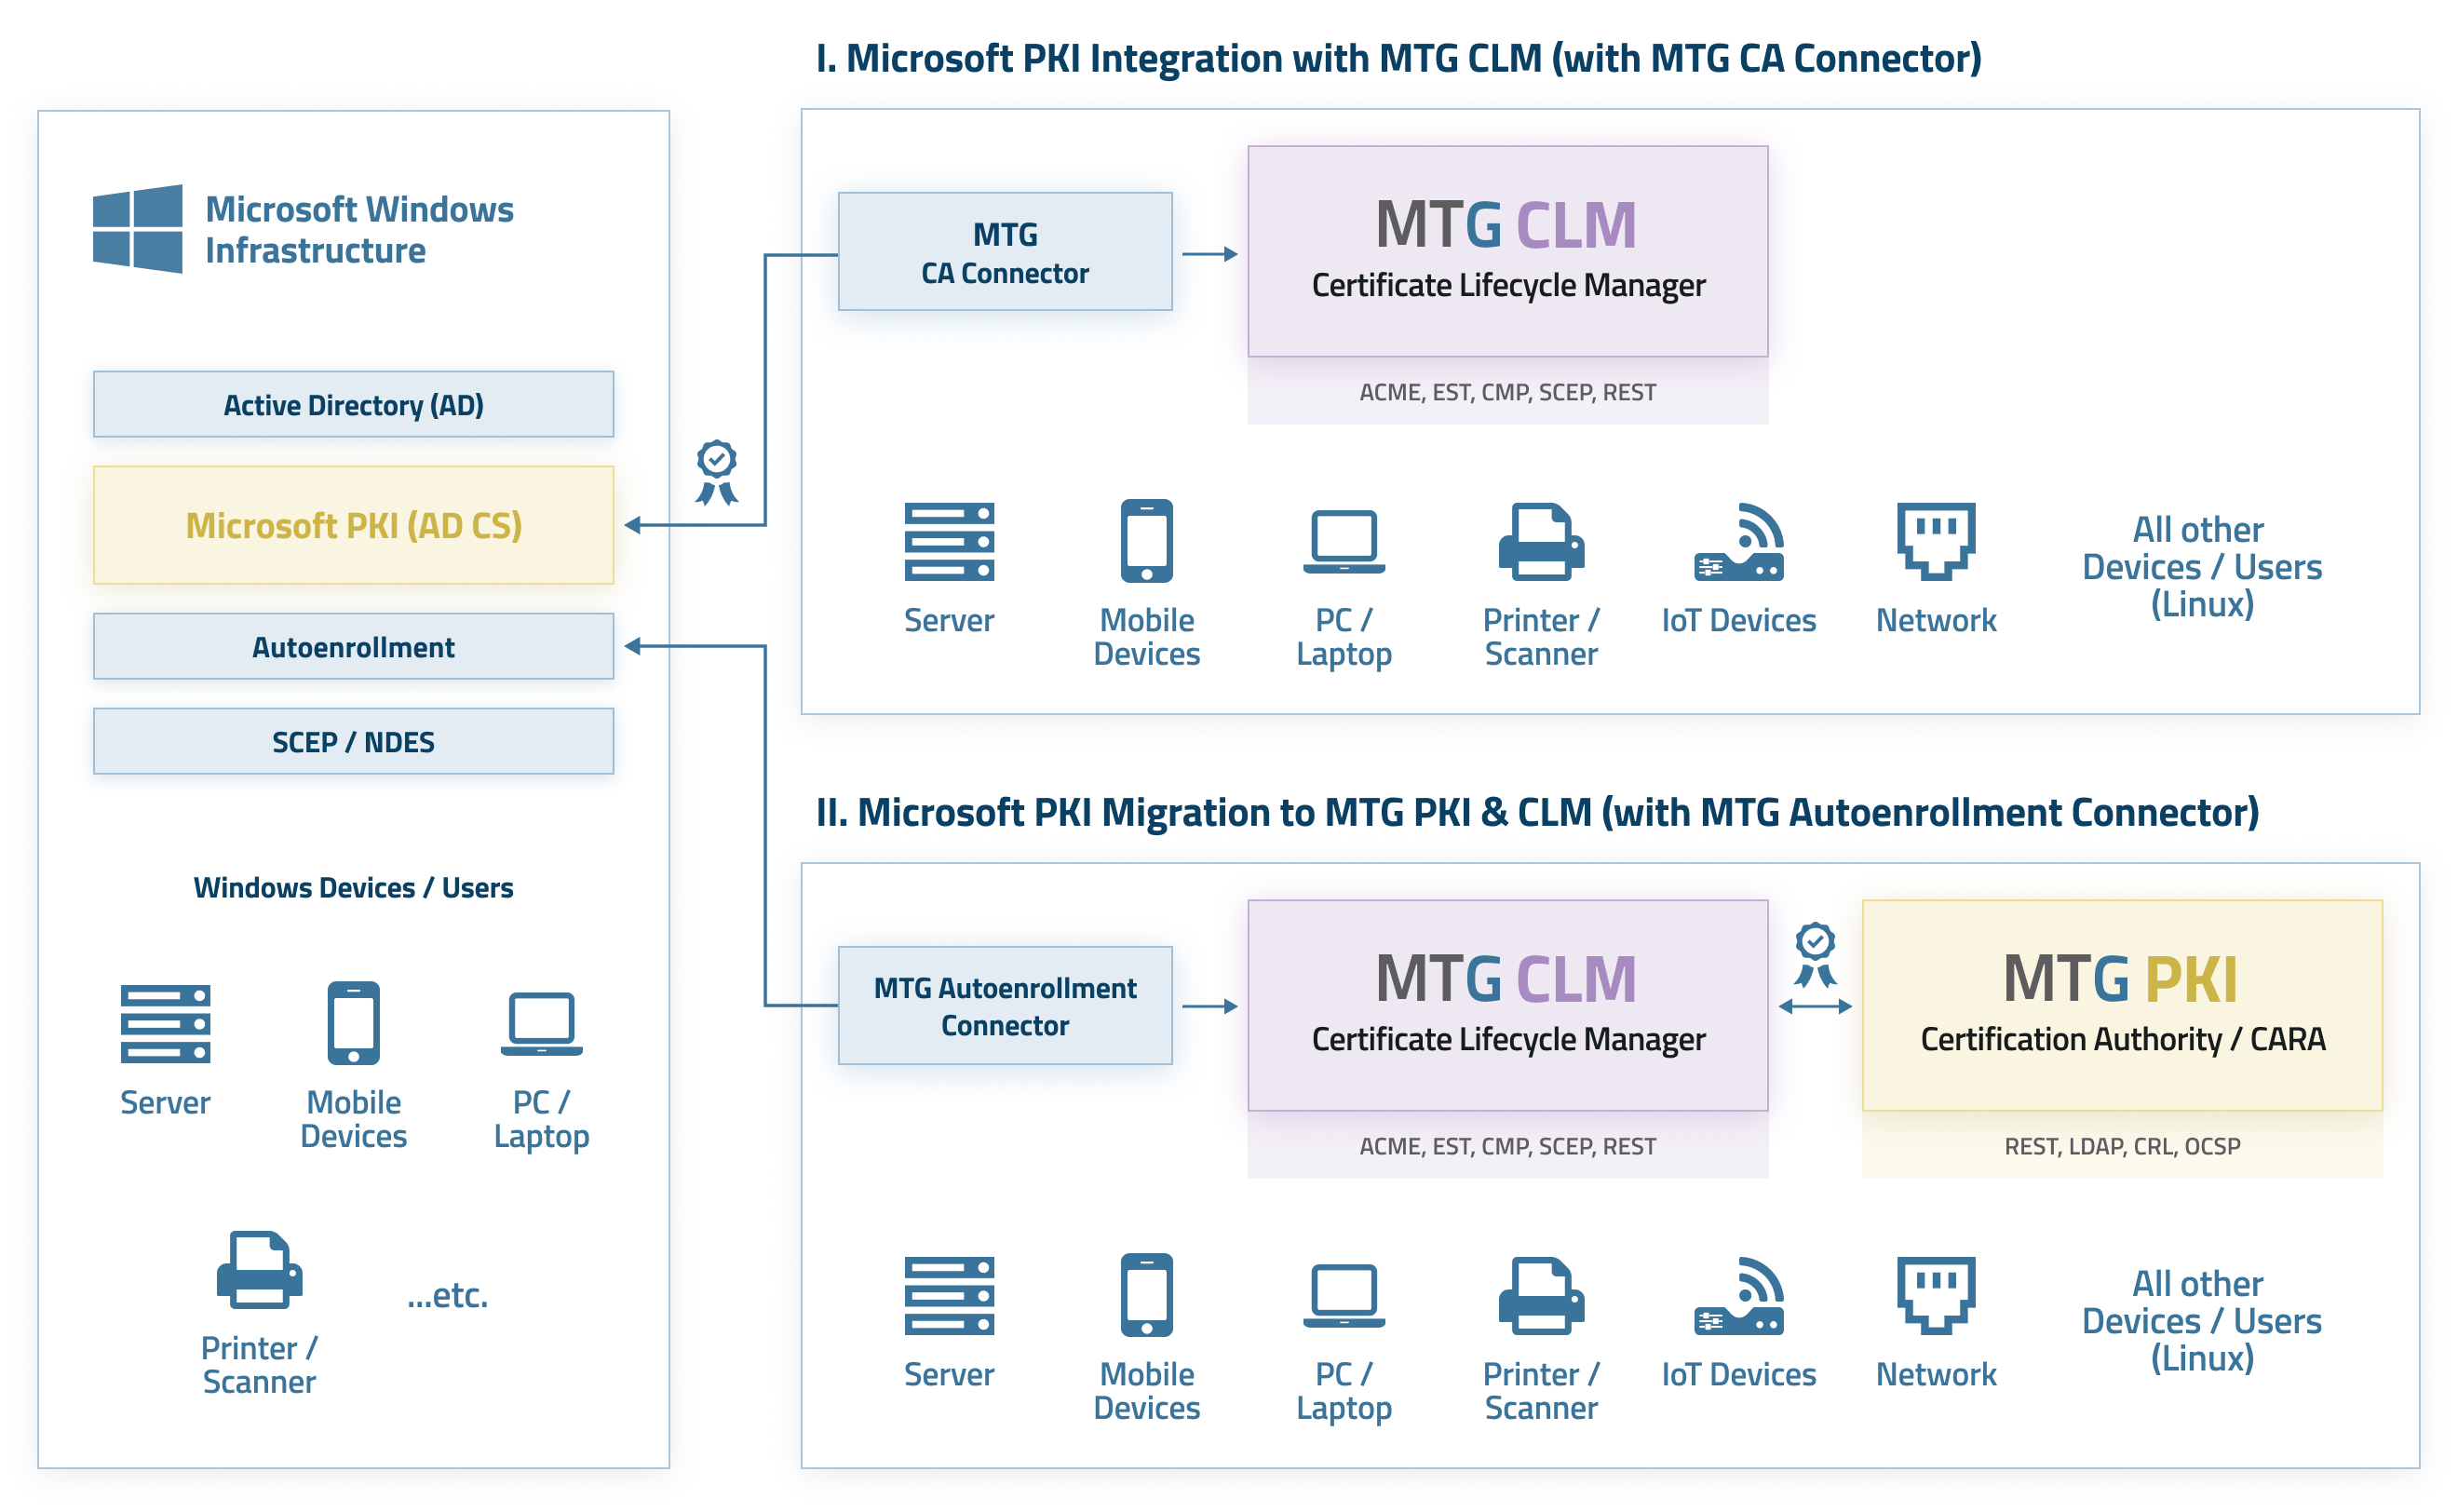
Yes, you can replace your Microsoft PKI with MTG Corporate PKI. Alternatively, you can continue operating your existing Microsoft PKI and connect it to MTG CLM. This allows you to use your existing Microsoft CA for additional use cases outside the Windows environment, such as the automated issuance of Linux server certificates via ACME.
For customers already using a Microsoft PKI based on AD CS, there are two options:
- Connect and continue operating Microsoft PKI (AD CS): The existing Microsoft CA remains the issuing PKI and is connected to MTG CLM through the Microsoft CA Certificate Provider. Certificate processes can then be centrally managed and automated through MTG CLM.
- Migrate Microsoft PKI (AD CS): With the MTG Auto-Enrollment Connector, Microsoft AD CS can be replaced as the issuing PKI by MTG Corporate PKI. Established Windows autoenrollment processes can continue to be used. Depending on the existing Active Directory and PKI configuration, preparatory configuration steps and, where necessary, additional adjustments may be required.