Five reasons why it simply fits.
Ready in minutes.
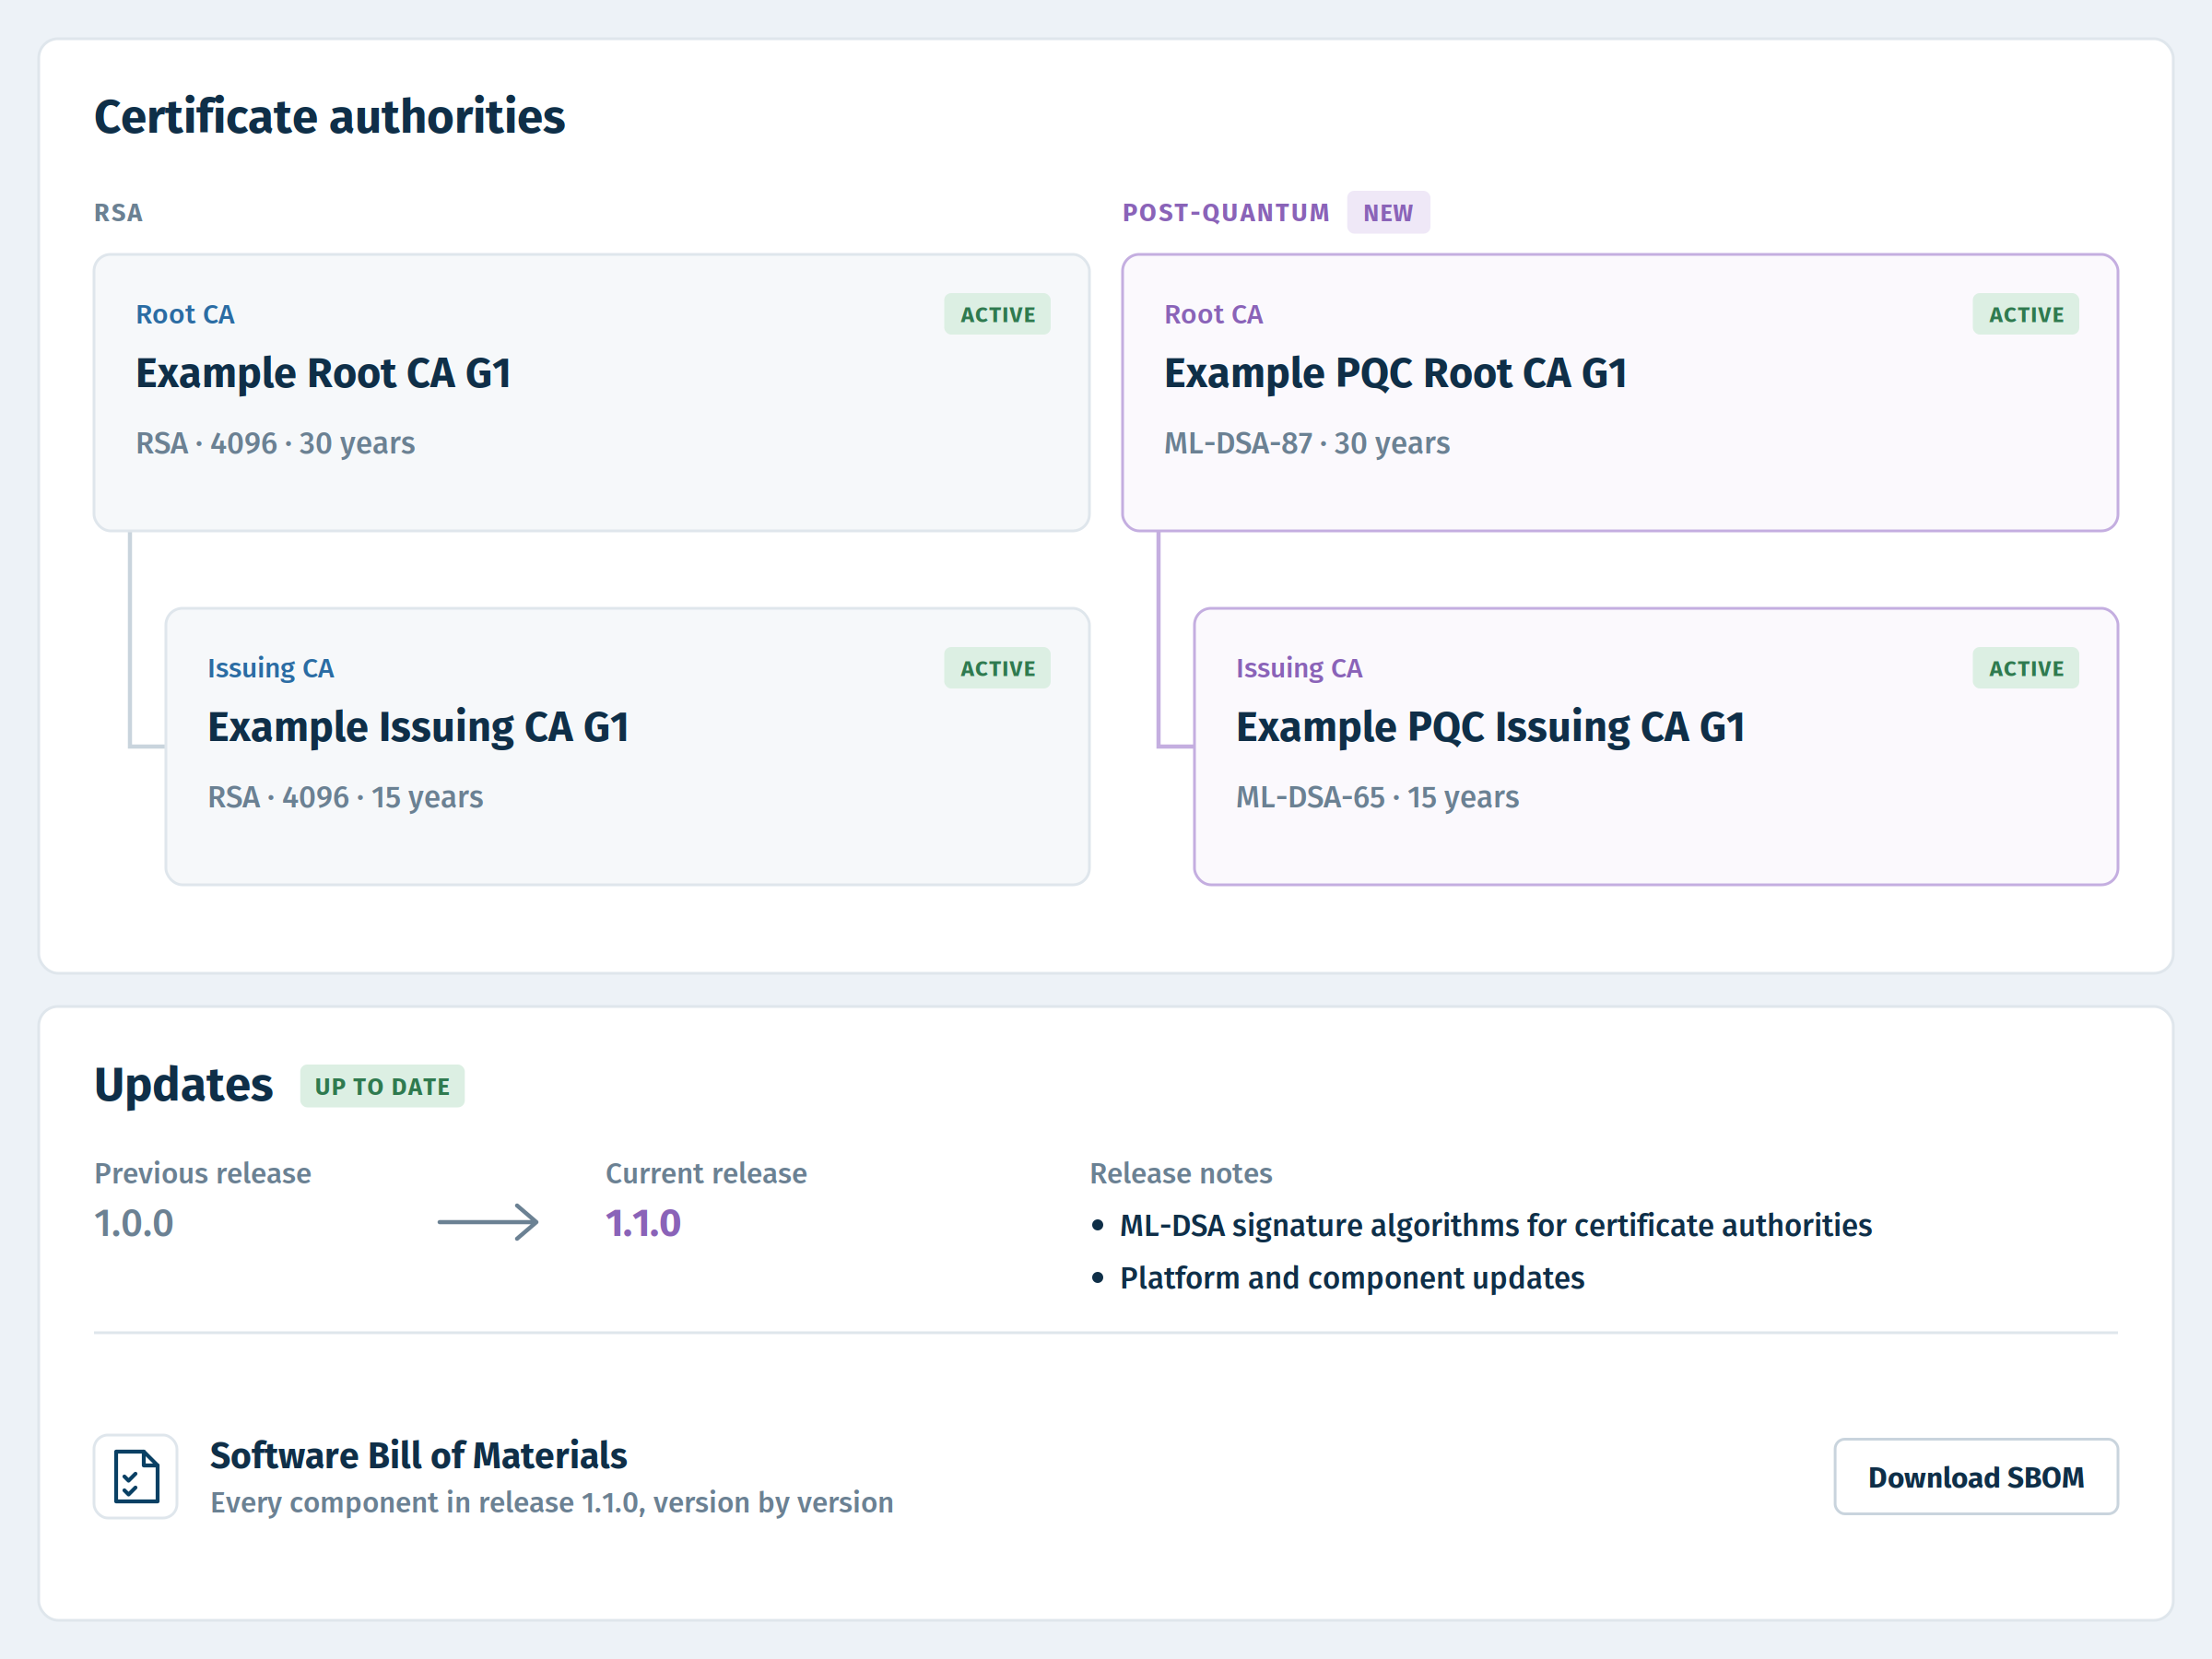
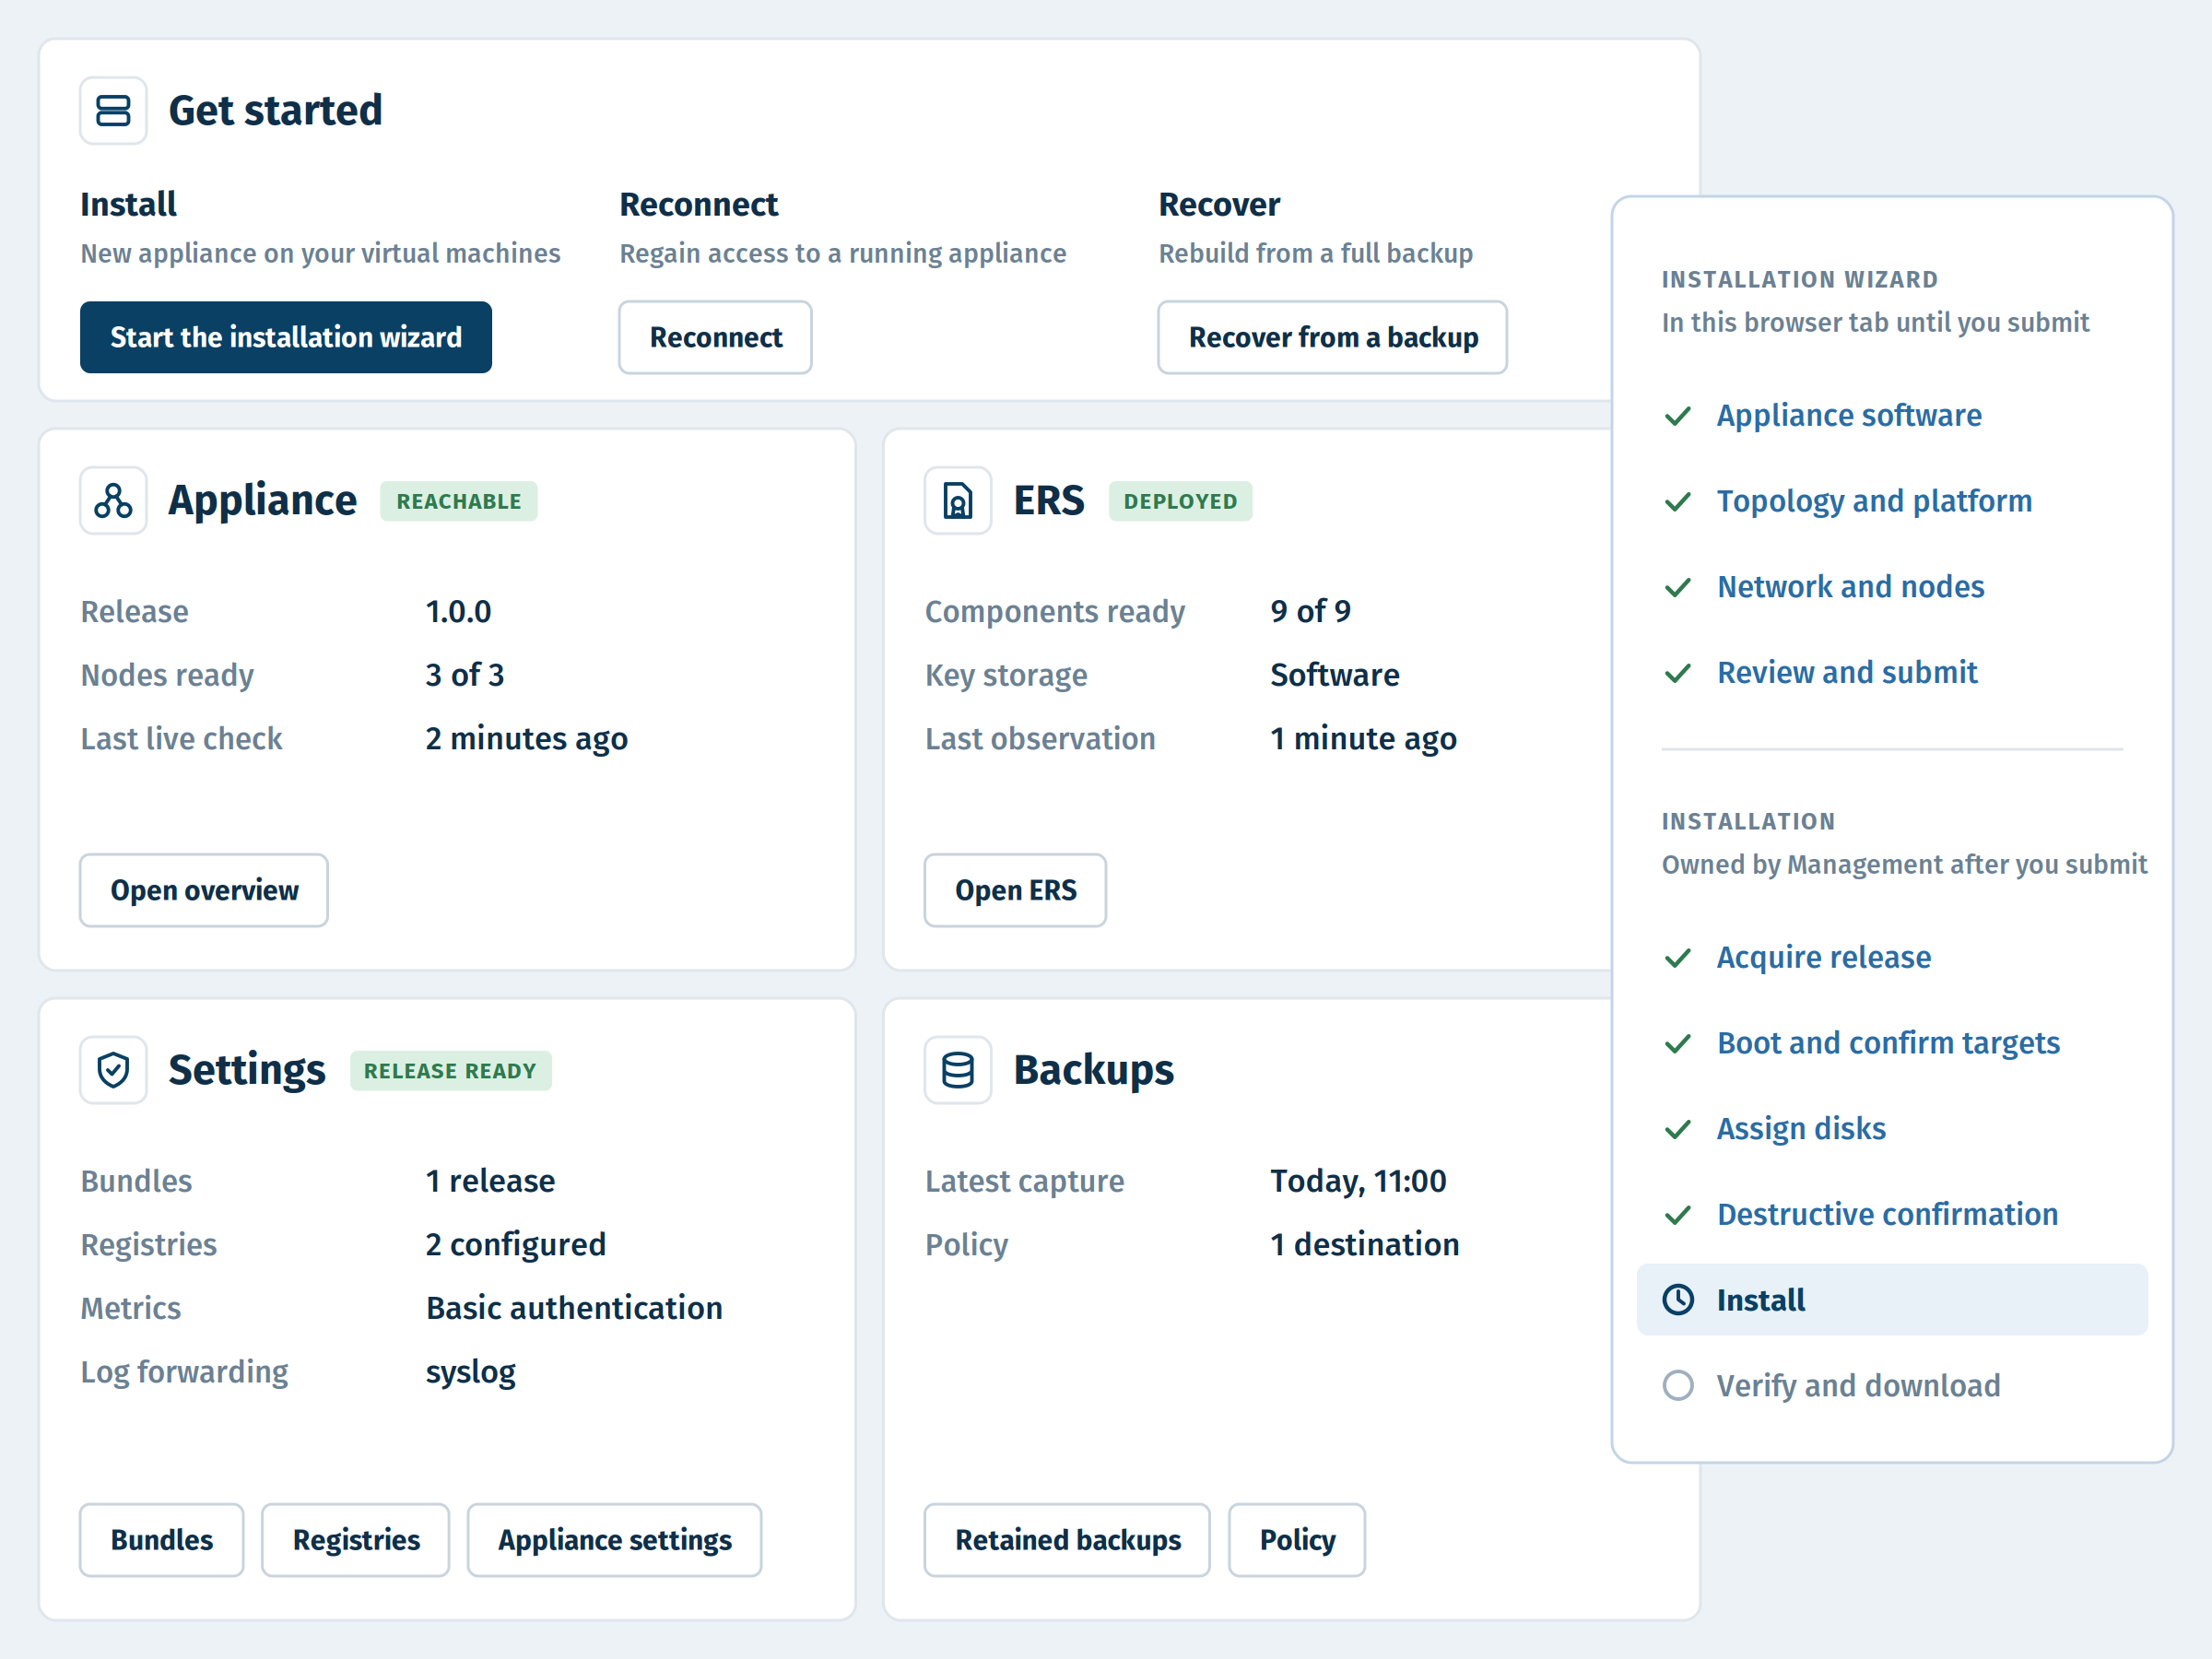
The appliance largely sets itself up. A wizard guides you step by step through all the important decisions until your first certificate is issued. No consulting project, no long implementation period, and none of the costs of a traditional implementation project.
PKI without PKI specialists.
Secure default settings and a clear, modern interface take the complexity off your team's hands. The solution can be integrated into your existing Microsoft environment. Common protocols such as ACME, EST, SCEP, and CMP let you automate certificate processes. This way, your IT runs the PKI day to day without any cryptography expertise.
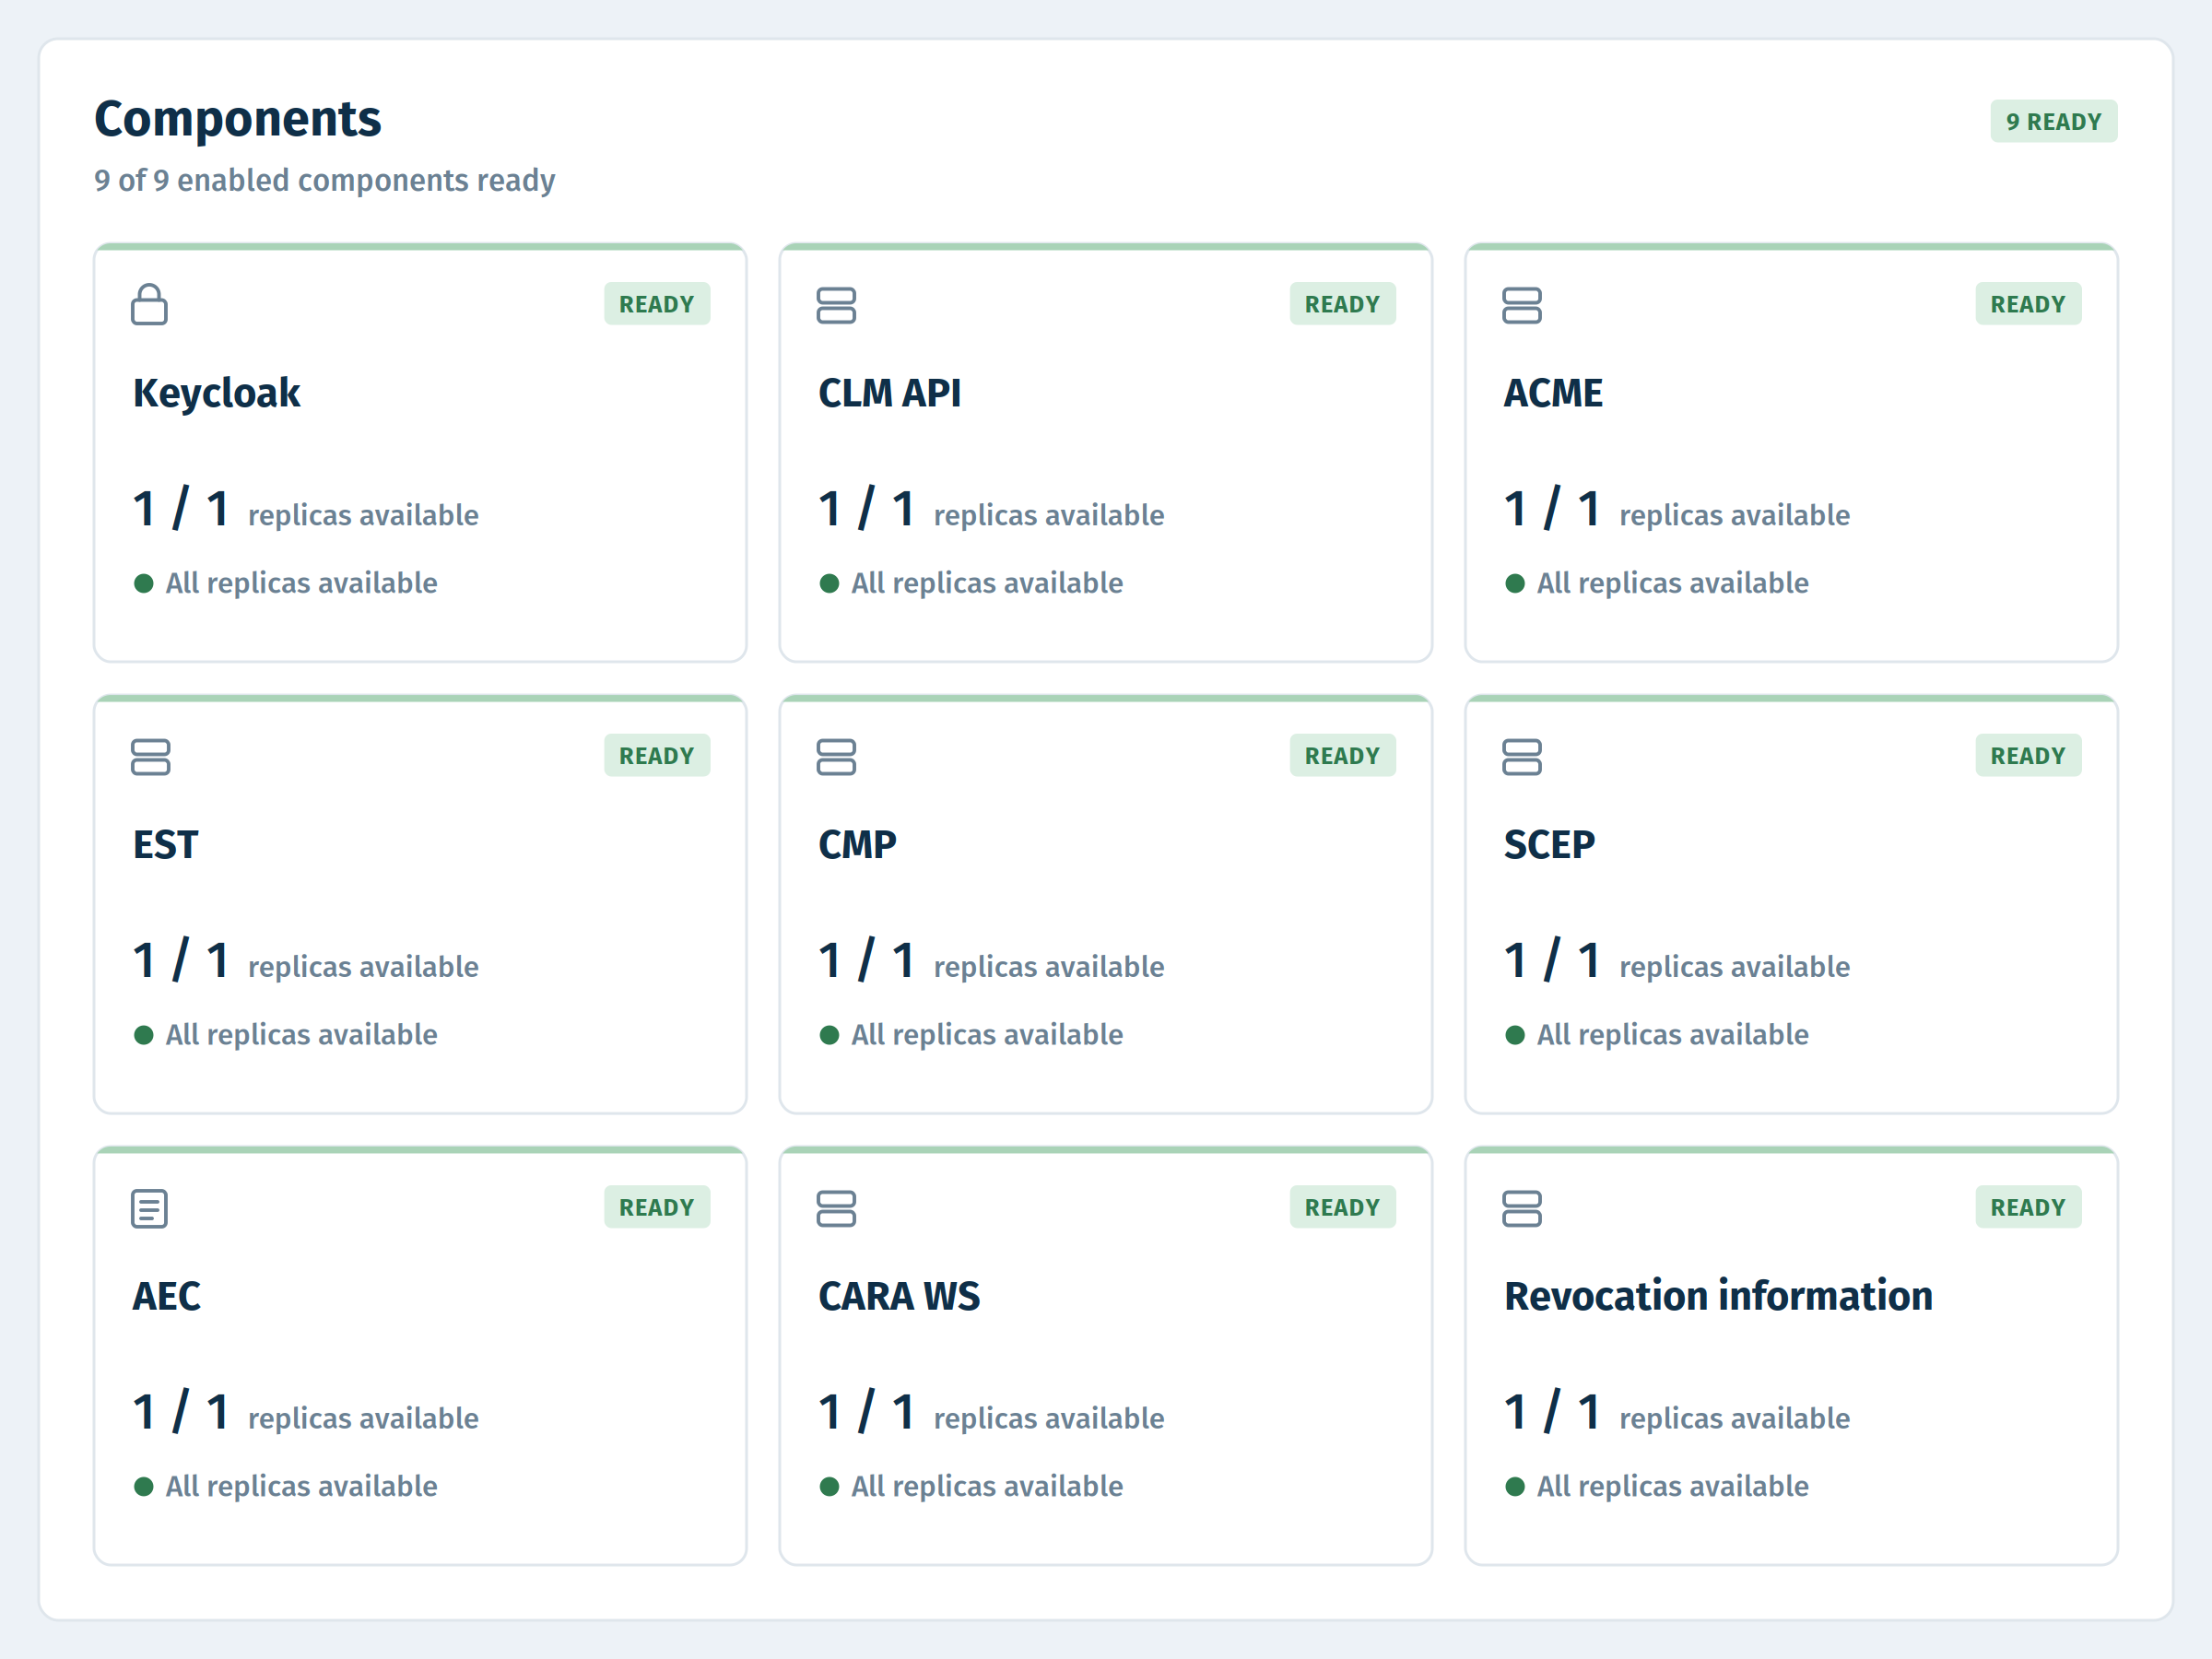
High availability, already built in.
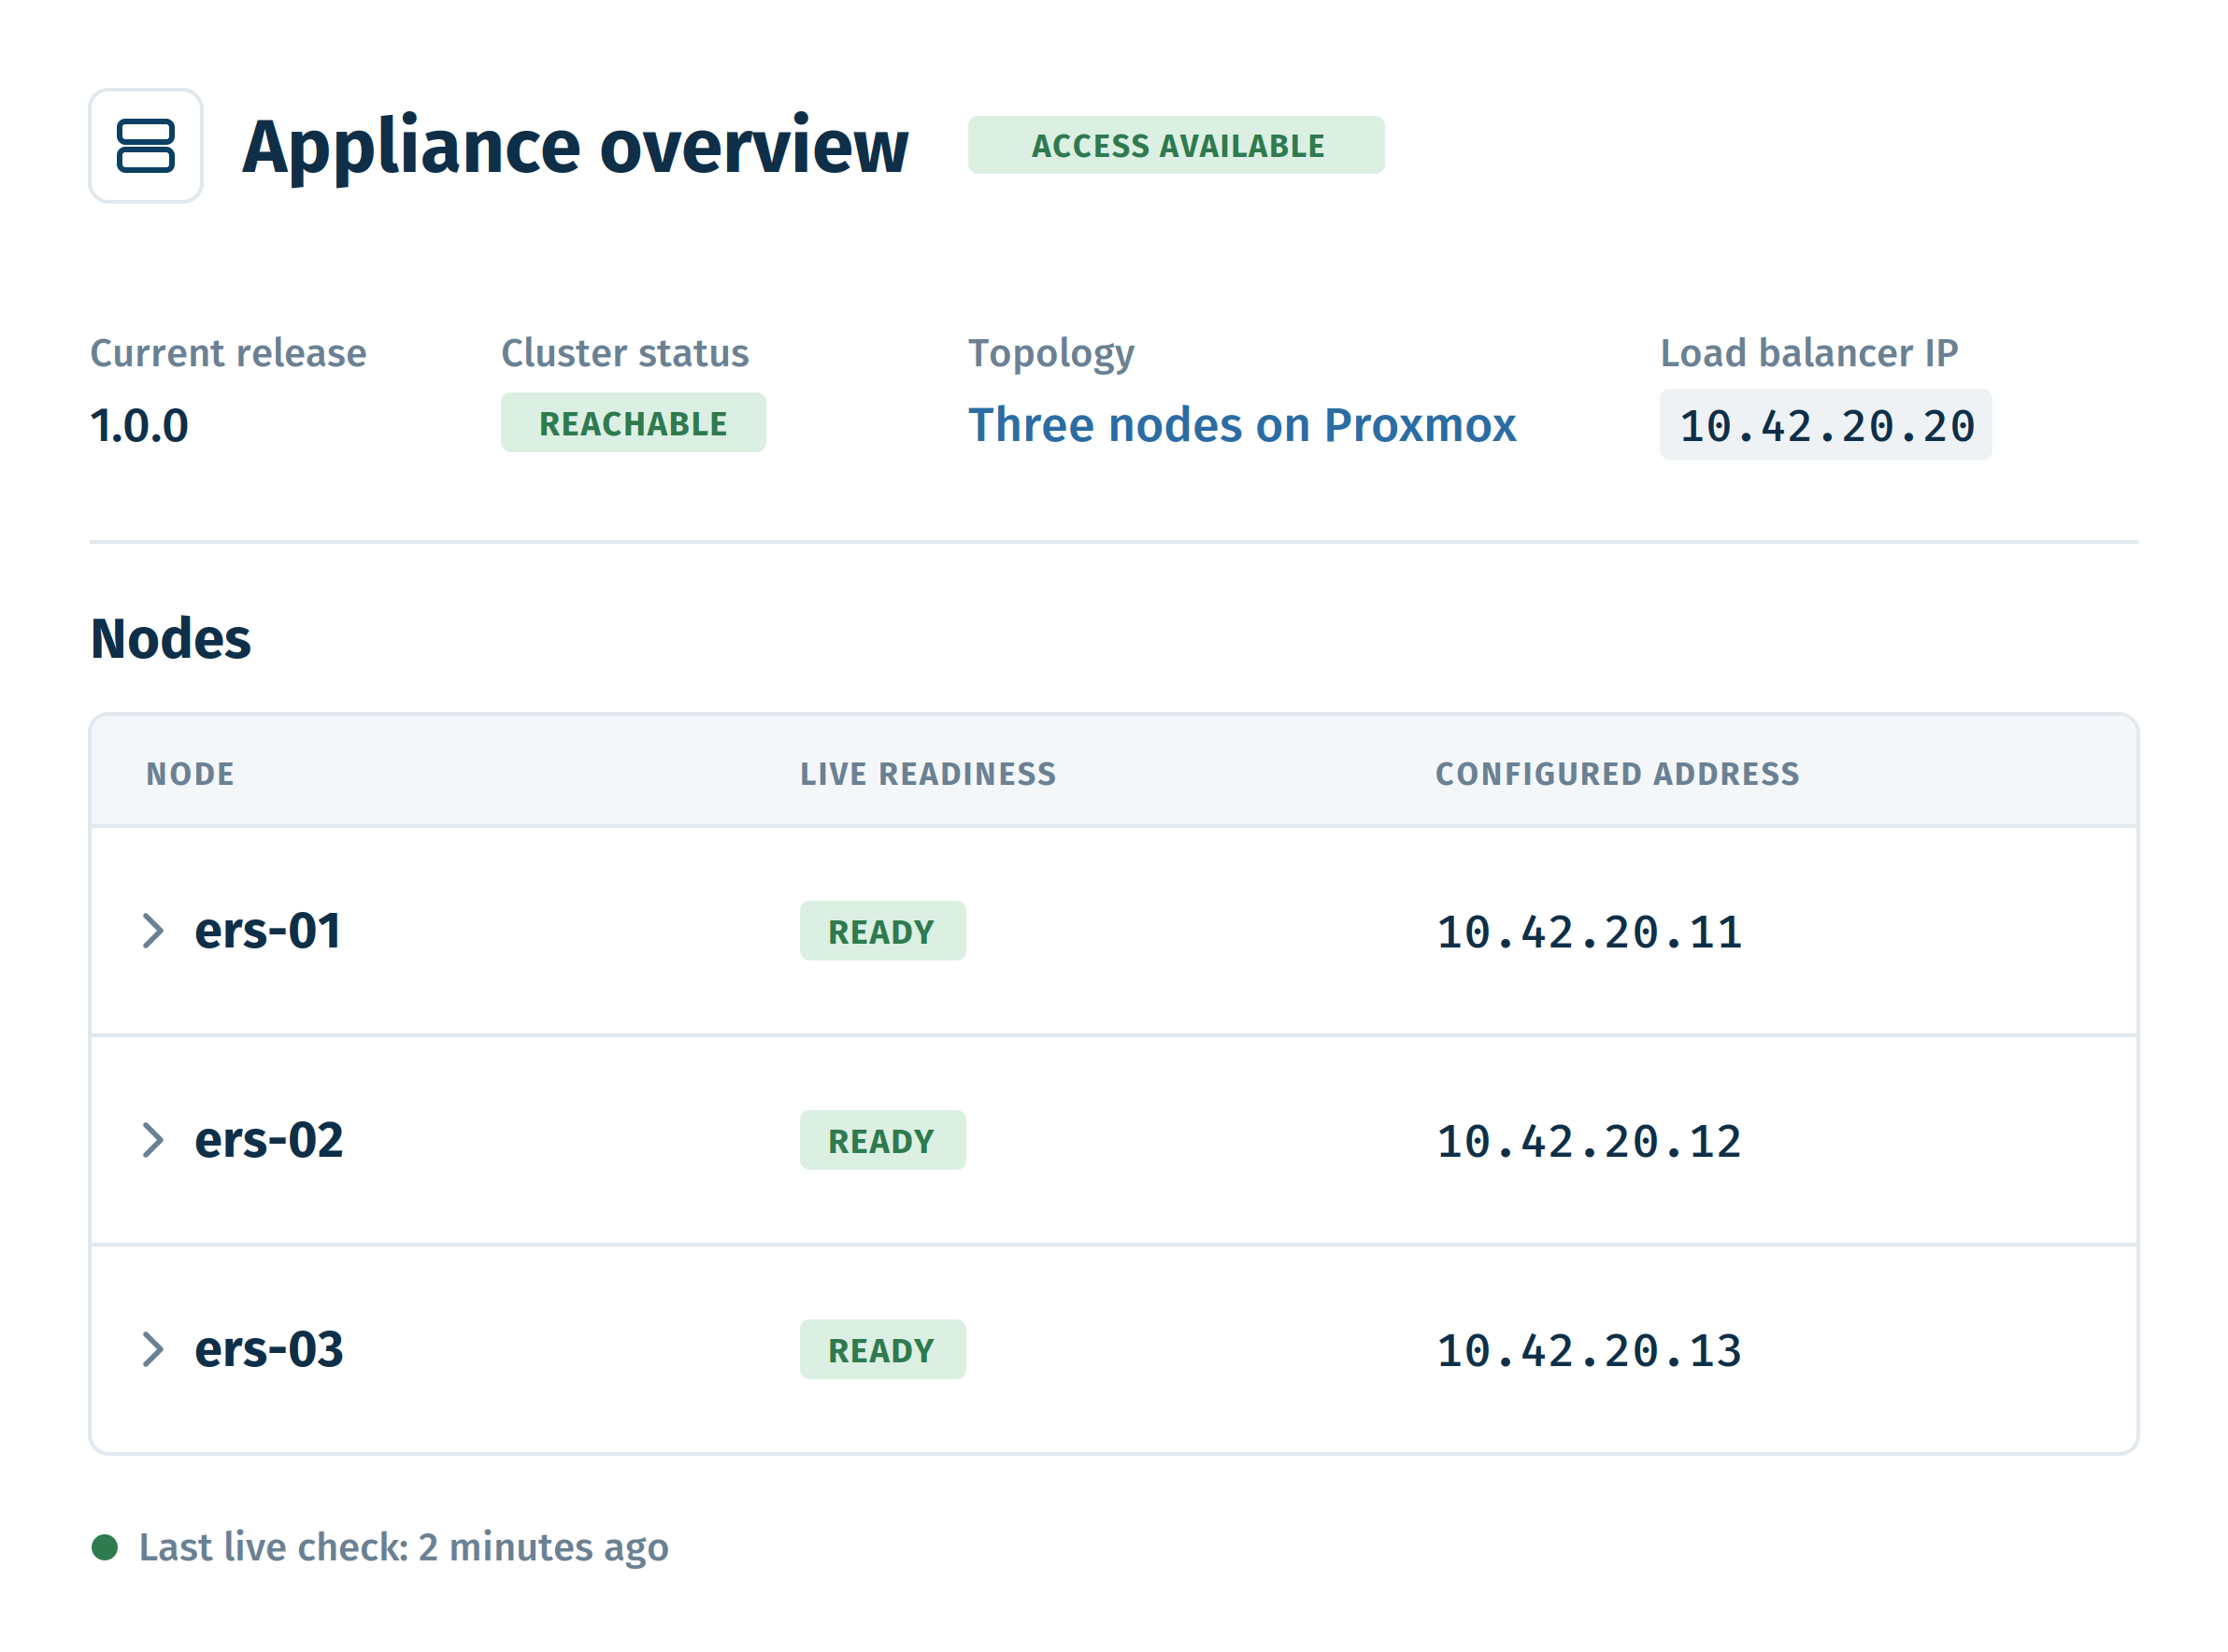
If a node fails, your certificate services continue to run without interruption. Clustering, backup and restore, monitoring, and central logging are already integrated. Start small and grow to several million certificates – without migration and without changing systems.
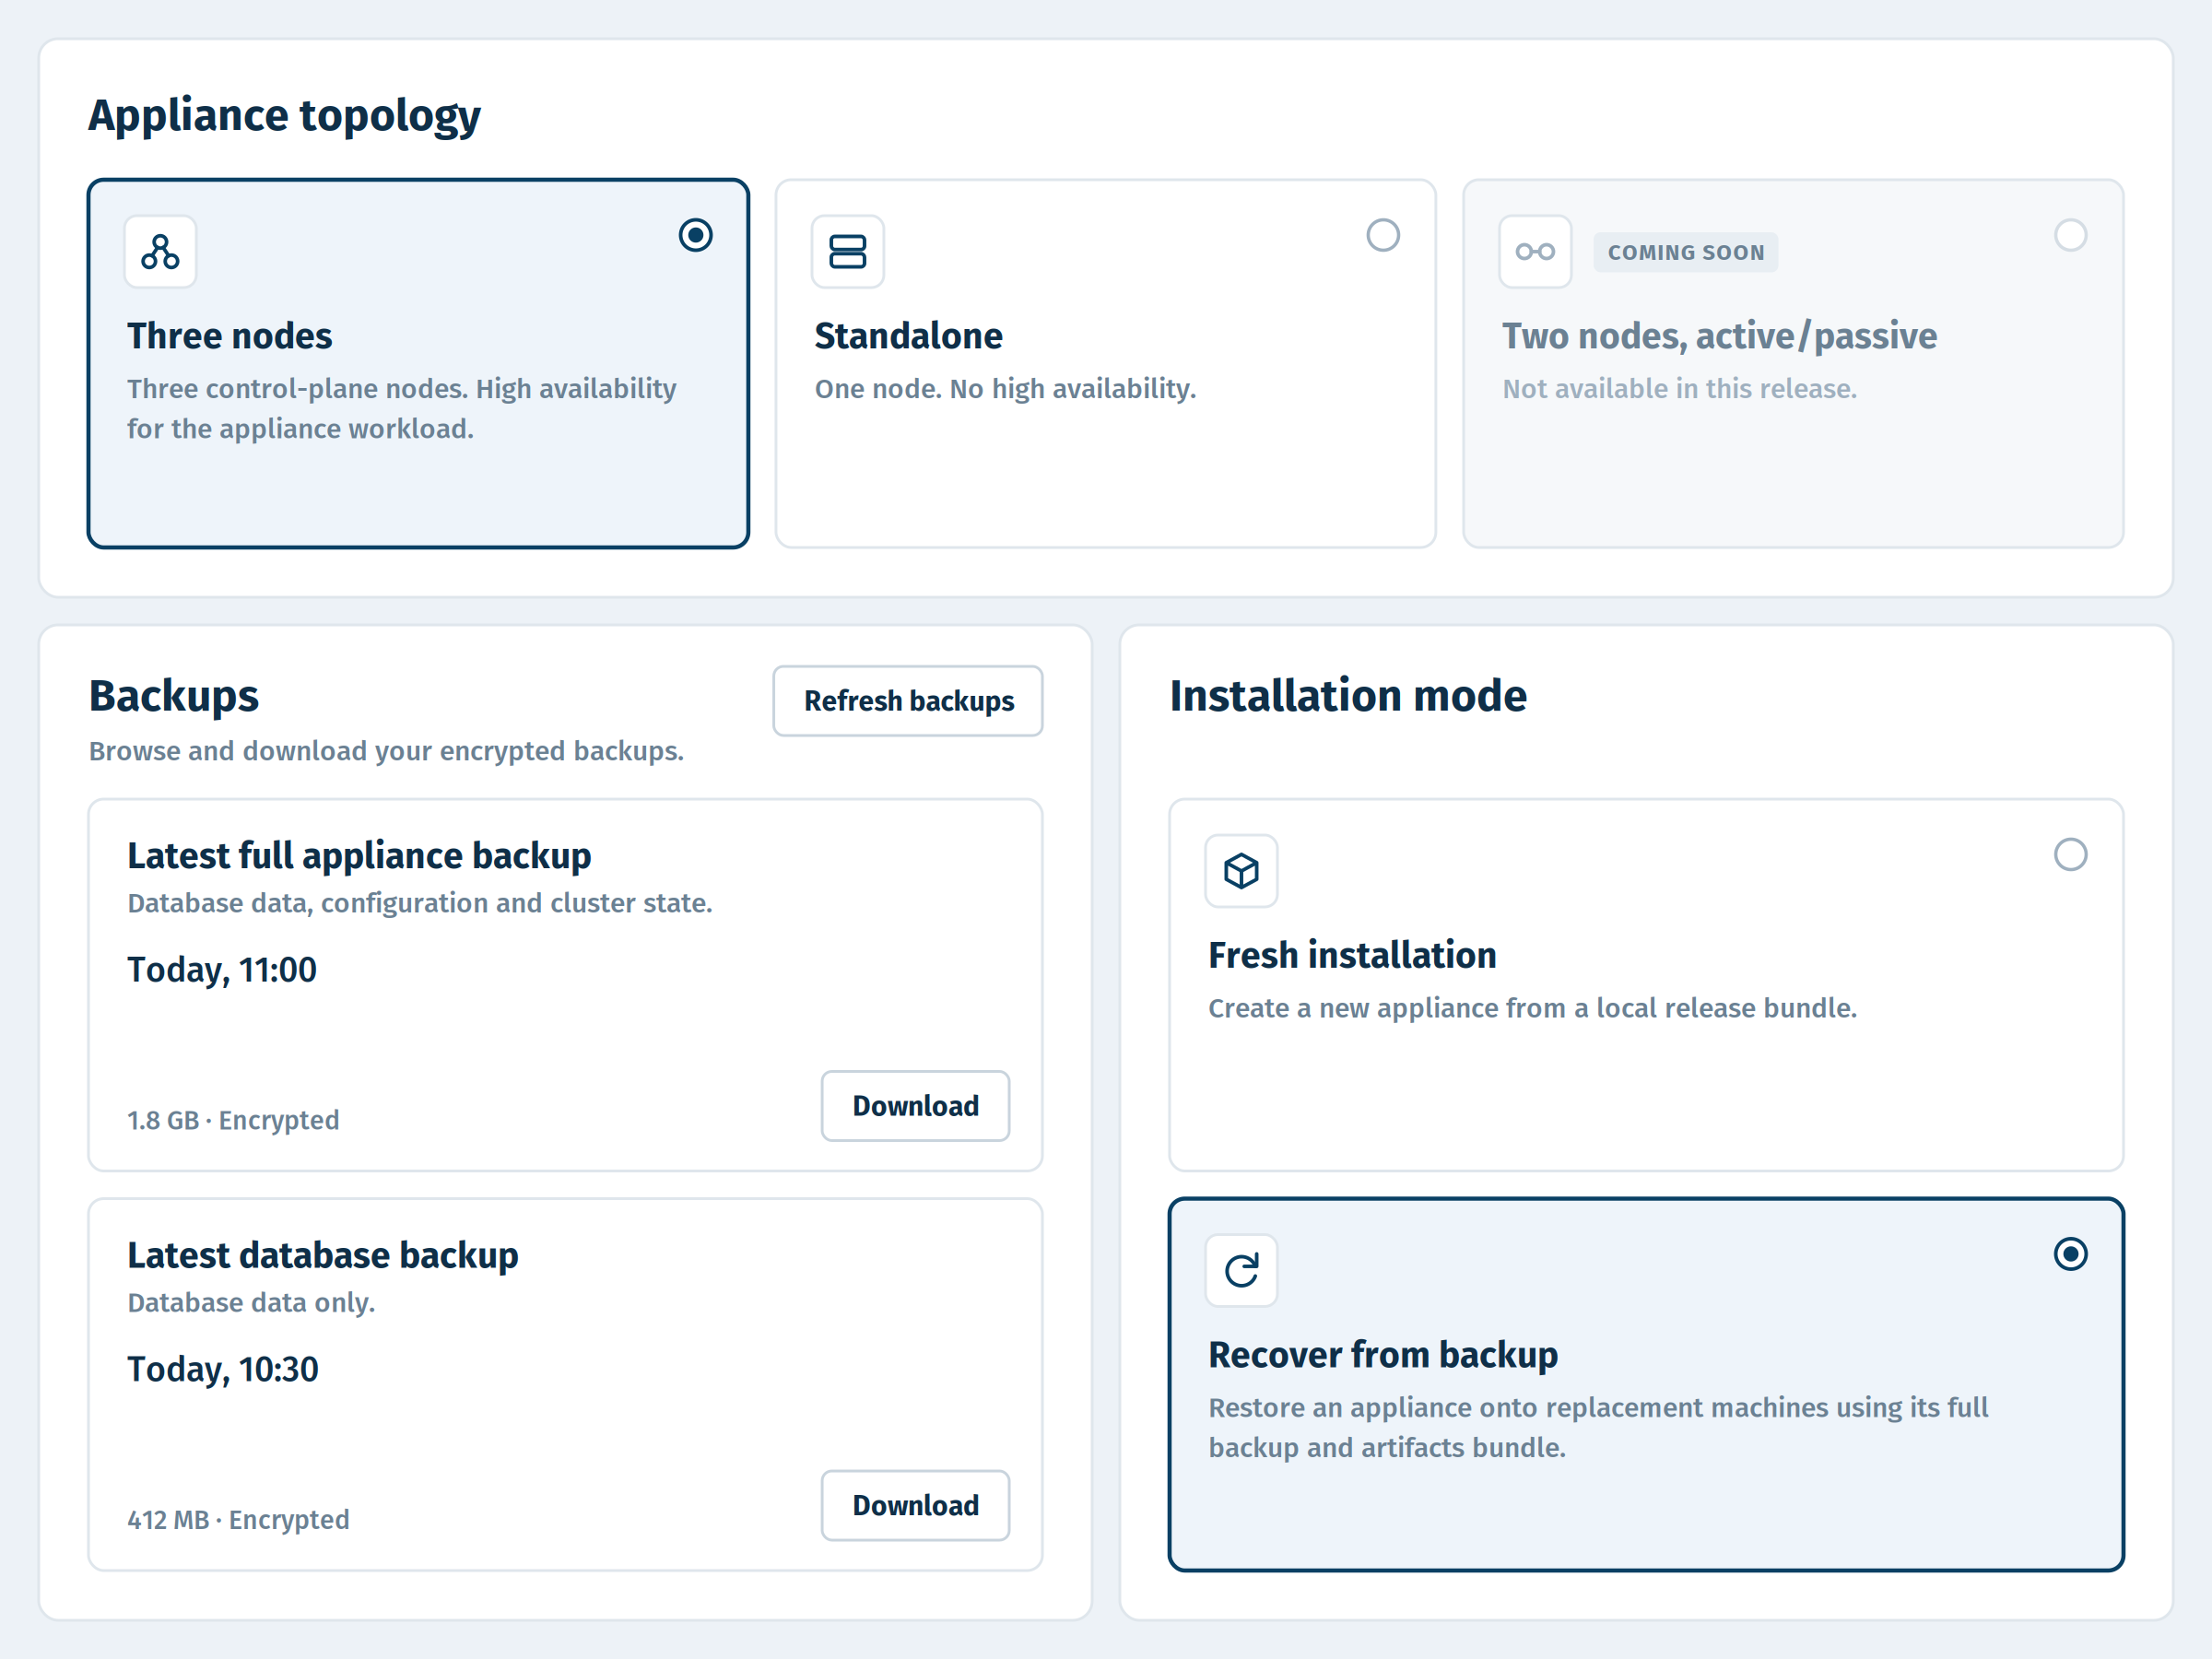
Runs wherever your IT runs.
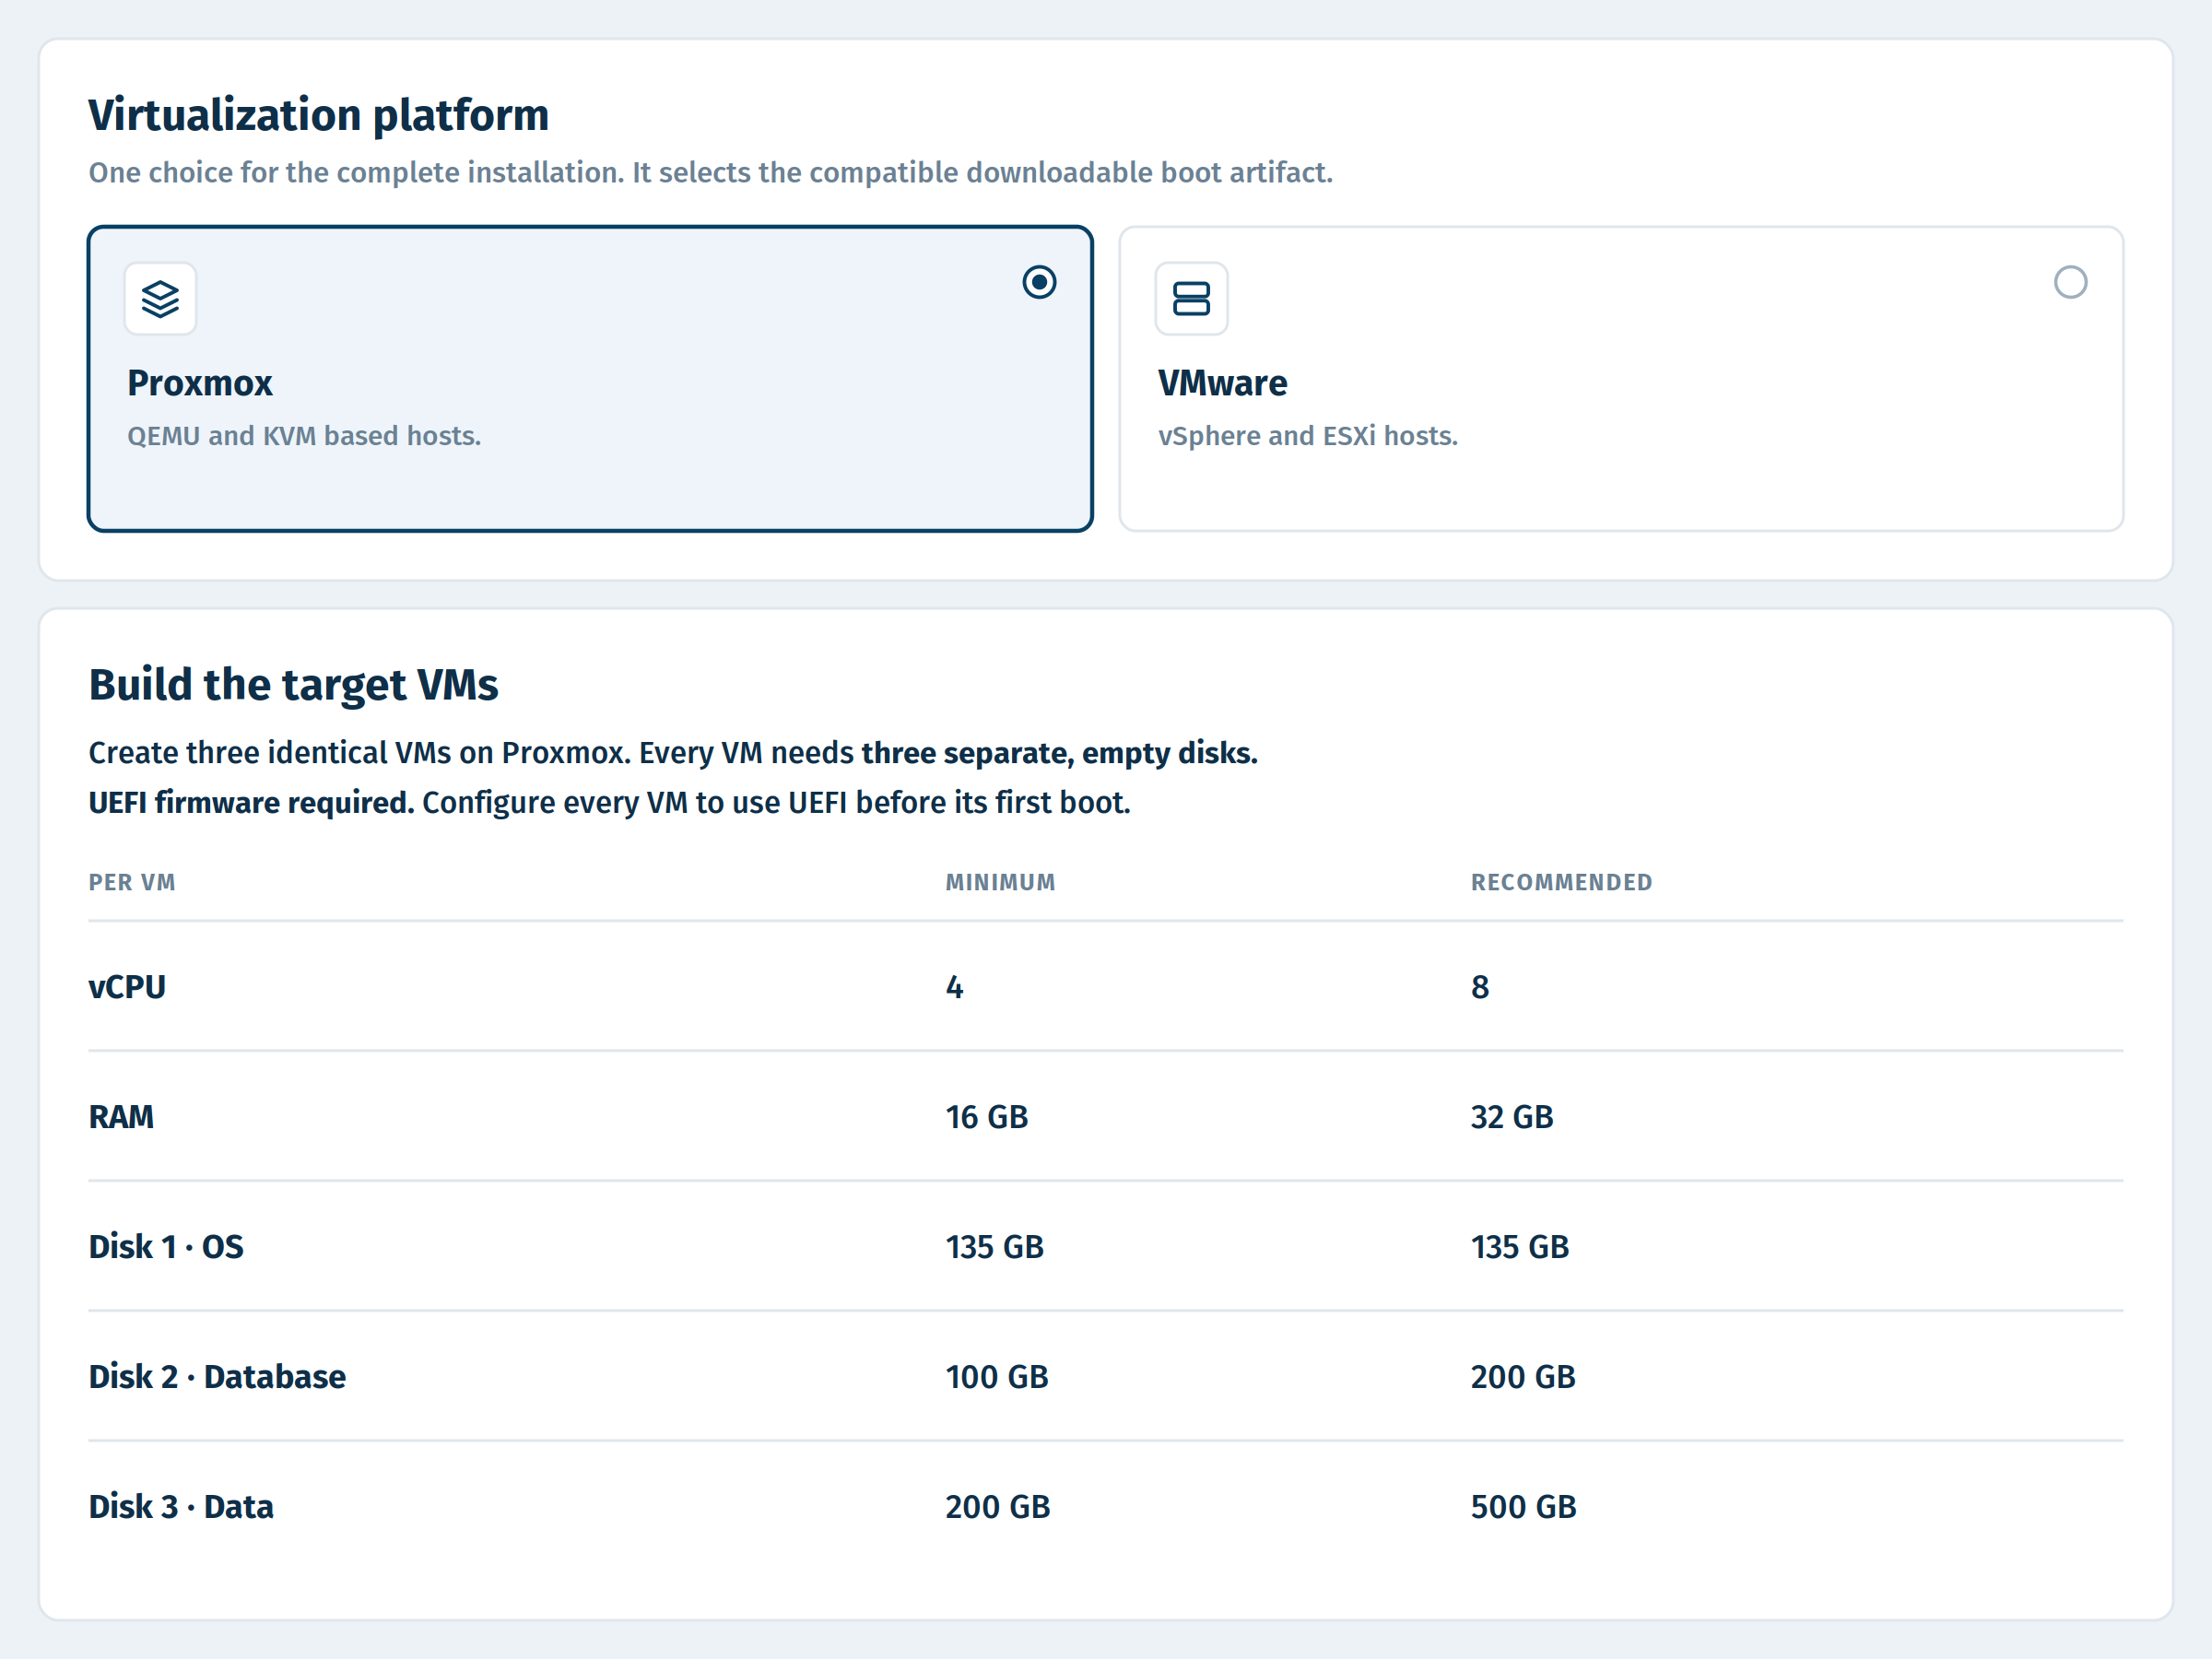
Whether in your own data center on VMware, Proxmox, KVM, Hyper-V, or Nutanix, in isolated networks without internet access, or with cloud providers such as AWS, Azure, Google Cloud, or STACKIT: the same software runs everywhere with the same license. Your keys and data stay where you decide, and under your control.
Built for the coming decades.